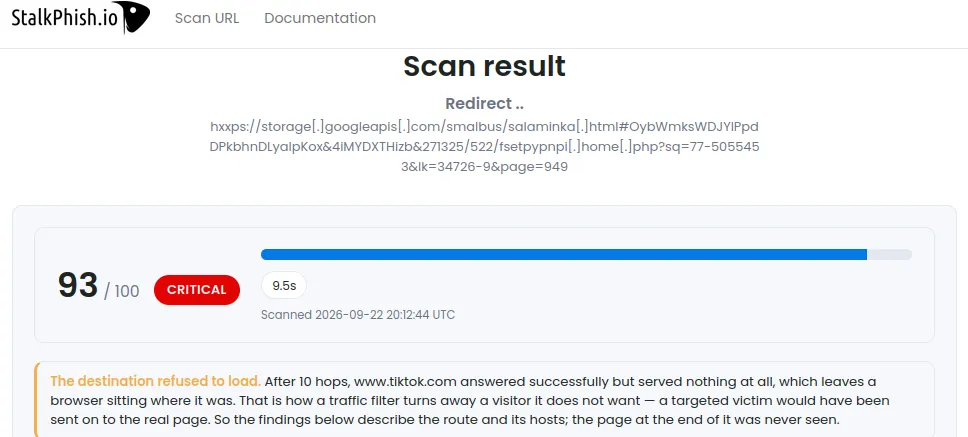
Ce lien est-il du phishing ? Découvrez le scanner d’URL StalkPhish (bêta fermée)
Vérifier un lien suspect sans l’ouvrir : le scanner d’URL StalkPhish suit redirections et cloaking, et donne un score de phishing argumenté. Bêta fermée.
Catégorie

Vérifier un lien suspect sans l’ouvrir : le scanner d’URL StalkPhish suit redirections et cloaking, et donne un score de phishing argumenté. Bêta fermée.

Brand protection, SOC enrichment, threat hunting, Telegram exfiltration tracking: eight practical ways to use the StalkPhish API against phishing and fraud.

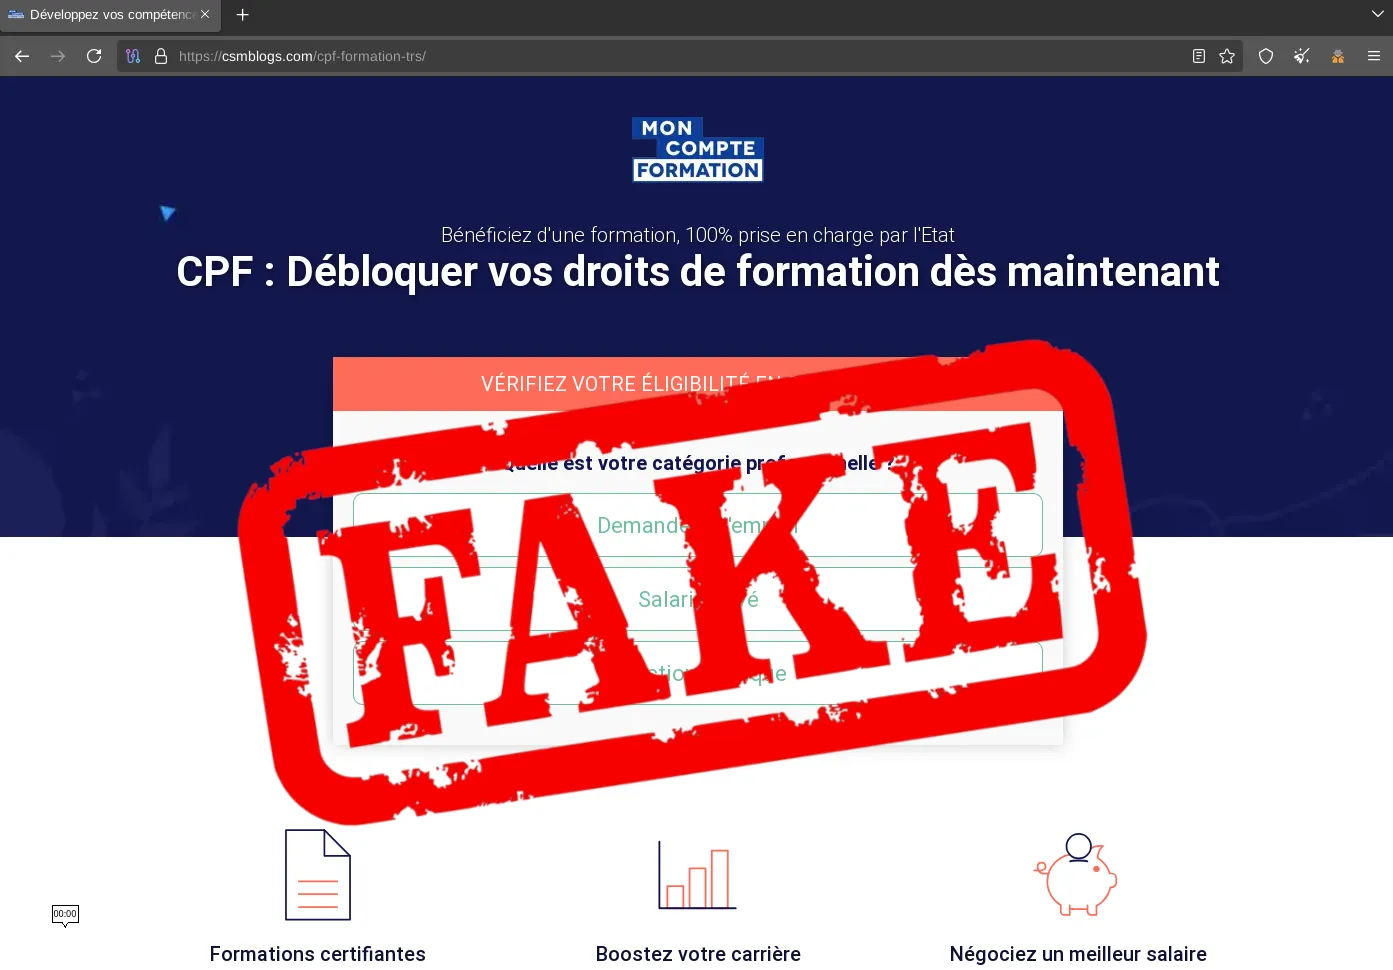
Analysis of the 'Lead' phishing kit impersonating MonCompteFormation (CPF), found in December 2024: pages, PHP scripts, logs and Telegram traces.

StalkPhish.io now classifies the phishing kits it collects by family, using the open source PhishingKit-Yara-Rules, to speed up qualification and investigation.

The StalkPhish.io Professional plan: 5,000 API requests a day, 6 months of history, and exclusive threat actor tracking and brand targeting.

Analysis of the 'Don' phishing kit impersonating Caisse d'Epargne (BPCE group), downloaded by StalkPhish.io in December 2023: structure and configuration.

Plongée dans un réseau de « scama » francophone qui propose des campagnes de phishing clés en main à 10 € contre Netflix, Société Générale, Ameli ou Crit'Air.

Launch of the StalkPhish.io Standard plan: SSL/TLS certificate data, Google Safe Browsing status, phishing score and searches in page titles.

Use case: detect phishing campaigns early by hunting phishing pages with StalkPhish, combining several data sources to find and take down sites faster.

A minimalist LinkedIn phishing kit written in Chinese: three PHP pages that email the stolen credentials, probably derived from a kit sold by Fudsender.

How to use the StalkPhish.io analyzer in IntelOwl, the open source threat intelligence platform, to enrich observables and speed up phishing analysis.