PhishingKit-Yara-Rules
YARA rules to identify phishing kits from their ZIP archives. Integrated into VirusTotal’s detection engine.
Open Source
Community
We build and maintain free tools used by analysts worldwide to hunt phishing kits.
YARA rules to identify phishing kits from their ZIP archives. Integrated into VirusTotal’s detection engine.
The phishing kits stalker: finds kit URLs in OSINT sources, downloads sources and extracts exfiltration emails.
Spots phishing kits reusing your own website files by analysing referers in your web server logs.
A collaborative glossary of the slang used in French-speaking scam and phishing networks, from Allo to Vouch.
StalkPhish.io now classifies the phishing kits it collects by family, using the open source PhishingKit-Yara-Rules, to speed up qualification and investigation.
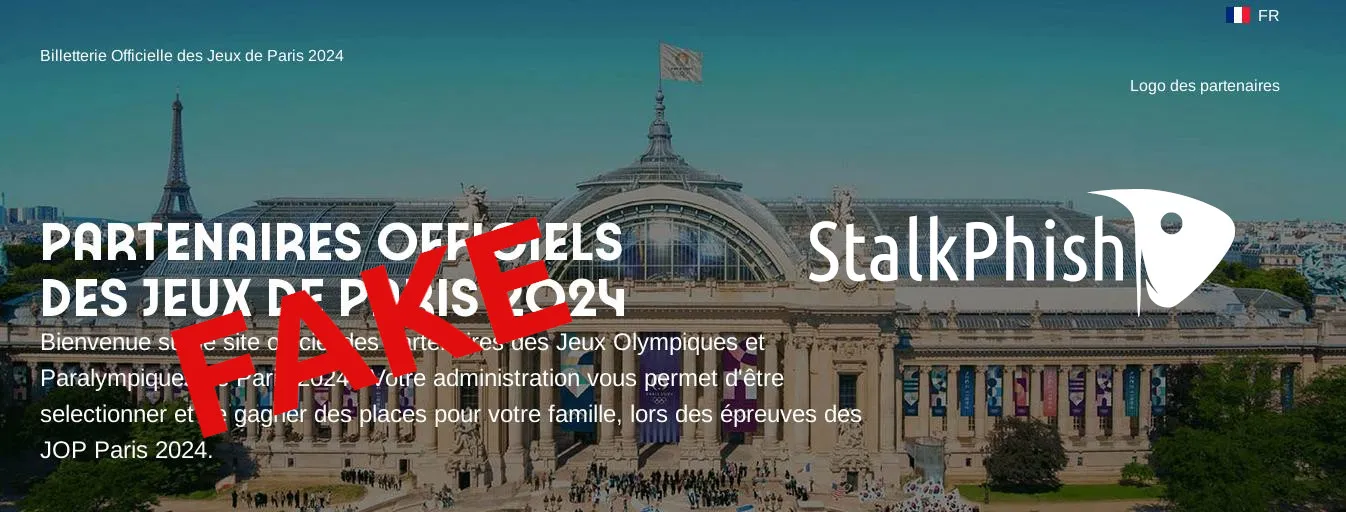
Phishing sites impersonating the Paris 2024 Olympic and Paralympic Games, spotted by StalkPhish.io in June 2024 to steal personal and banking data.
Analysis of the 'Don' phishing kit impersonating Caisse d'Epargne (BPCE group), downloaded by StalkPhish.io in December 2023: structure and configuration.
Start with a free search, or talk to us about API access and custom intelligence for your brand.