· CERT
[StalkPhish.io] Phishing Kit family enrichment
Since last summer, StalkPhish.io , our advanced platform dedicated to combating bank fraud, phishing, and scams, has been upgraded with a system for…
900+ YARA rules to identify phishing kits from their ZIP archives, running in VirusTotal’s detection engine.
Clone the repository
$ git clone https://github.com/t4d/PhishingKit-Yara-Rules.git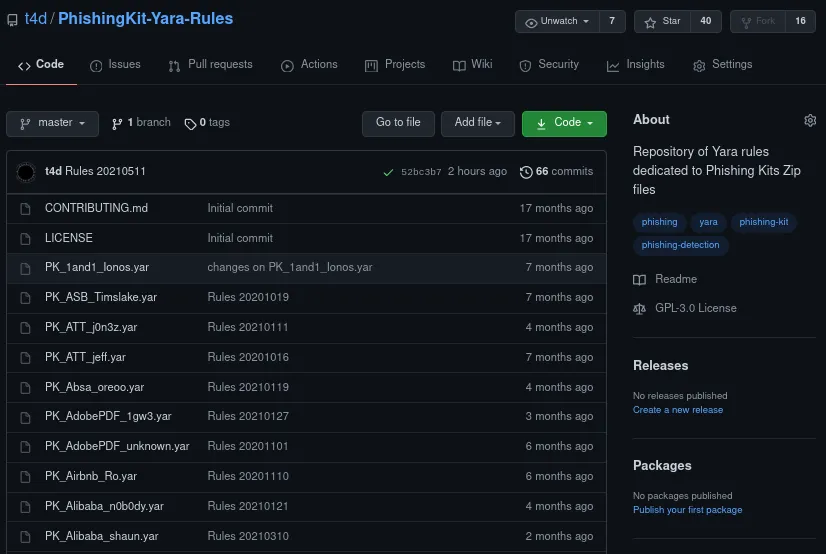
This comprehensive repository is dedicated to providing YARA rules specifically designed for detecting phishing kit zip files. The detection methodology is based on raw zip format analysis, focusing on identifying characteristic directory structures and file names within compressed phishing kits. Notably, these rules do not require yara-extend, as they operate directly on the raw zip file format to examine internal file and directory naming patterns.
The repository embraces open-source collaboration and welcomes contributions from the cybersecurity community. We encourage security researchers, threat analysts, and cybersecurity professionals to submit pull requests with their own rule sets. By sharing knowledge and detection techniques, we collectively strengthen our defense capabilities against evolving phishing threats.
The initial rule set was developed specifically for the PhishingKit-Yara-Search project, which provides a comprehensive framework for analyzing phishing kit zip files. This foundation has grown into one of the most extensive collections of phishing kit detection rules available to the security community.
For those interested in contributing to the project or developing custom rules, we recommend consulting the official YARA documentation for detailed guidance on rule syntax and best practices.
🔥 Still growing: as of October 2026, the repository holds 926 YARA rules, up from 850 in June 2025 and 750 in September 2024, with new rules added every week.
These comprehensive detection rules provide coverage for phishing kits targeting over 3️⃣0️⃣0️⃣ of the world’s most recognizable brands and commercial entities. This extensive coverage includes major technology companies, financial institutions, social media platforms, e-commerce sites, and government organizations that are frequently targeted by phishing campaigns.
The rules employ a straightforward yet effective approach to phishing kit identification by analyzing the internal structure of zip archives without requiring decompression. This method focuses on:
We actively encourage participation from the global cybersecurity community. Contributing to this project helps strengthen collective defense capabilities against phishing threats. Here’s how you can get involved:
All contributions should follow our established guidelines outlined in CONTRIBUTING.md. We maintain high standards for rule quality, documentation, and testing to ensure the repository remains a reliable resource for the security community.
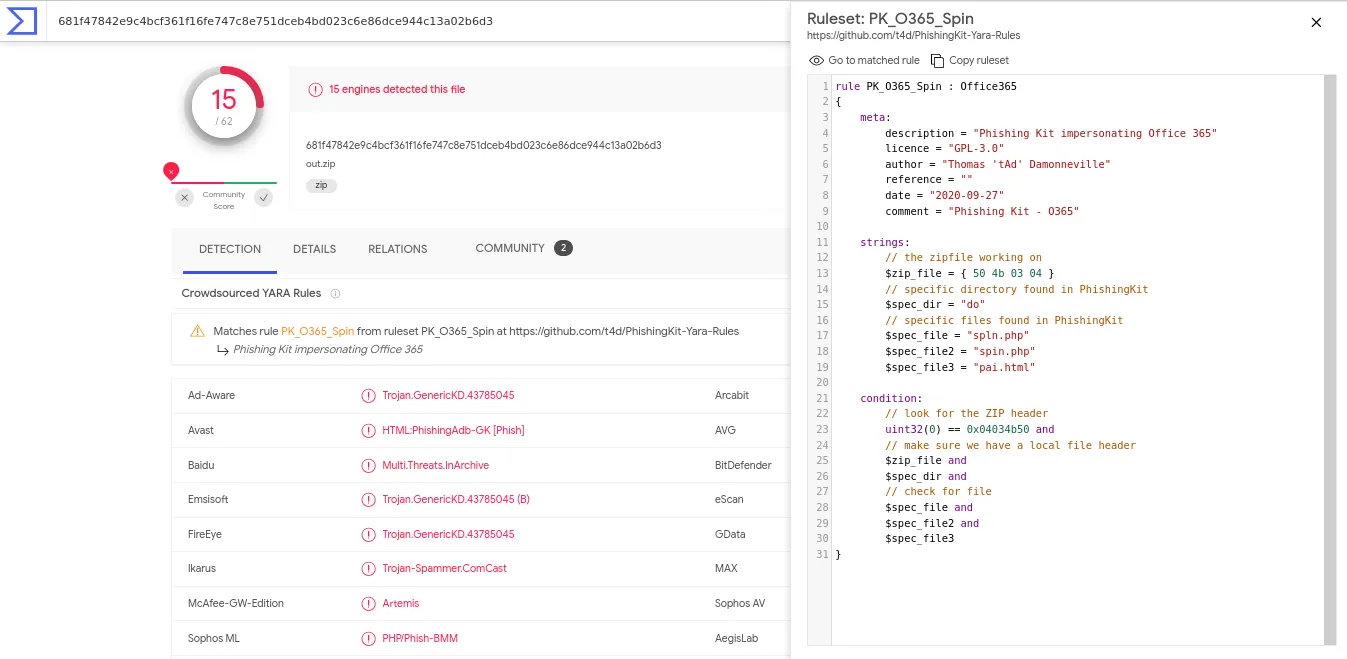
These rules have been integrated into VirusTotal’s threat detection engine, where they contribute to enhanced threat triage and detection capabilities. This integration demonstrates the rules’ effectiveness and reliability in production environments, as VirusTotal processes millions of samples daily from security researchers and organizations worldwide.
The PhishingKit-Yara-Rules are also seamlessly integrated into StalkPhish.io, our comprehensive phishing threat intelligence platform. This integration enables security teams to automatically qualify and categorize phishing threats with unprecedented precision. When StalkPhish.io detects a phishing kit in the wild, these YARA rules provide instant attribution and classification, helping analysts quickly understand the threat’s origin, target brands, and potential impact. This automated threat qualification significantly reduces analysis time and enables faster response to emerging phishing campaigns, making StalkPhish.io an essential tool for proactive phishing defense and threat hunting operations.
The repository has become an essential resource for:
🔗 GitHub Repository: https://github.com/t4d/PhishingKit-Yara-Rules
The repository is freely available under an open-source license, enabling widespread adoption and community collaboration. Regular updates ensure that the rule set evolves alongside emerging phishing threats and techniques.
Since last summer, StalkPhish.io , our advanced platform dedicated to combating bank fraud, phishing, and scams, has been upgraded with a system for…
This phishing kit impersonates Caisse D'Epargne , a French bank, of BPCE Group. This kit was downloaded at the beginning of December 2023, by our phishing…
Find a short analysis of the "Greatness" phishing kit used by a new Phishing as a Service infrastructure. Added some original IOCs for detection and hunting.
Start with a free search, or talk to us about API access and custom intelligence for your brand.