· StalkPhish.io
Is that link phishing? Meet the StalkPhish URL scanner (closed beta)
Check a suspicious link without opening it: the StalkPhish URL scanner follows redirects and cloaking, and gives a phishing score with evidence. Closed beta.
Your daily phishing and brand impersonation feed, with the threat-actor intelligence behind each campaign.
StalkPhish.io is our product, hosted at stalkphish.io: pricing, documentation and sign-up are there.
StalkPhish.io is the platform we built from ten years of collecting and dissecting phishing kits. Every day it pre-qualifies, crawls and analyses more than 60,000 suspicious websites, downloads the phishing kits left behind on their servers, and turns what it finds into data your team can act on: the malicious URL, the brand it impersonates, the hosting behind it and the channels the scammers use to receive stolen data.
Nearly 1,000 users, from SOC analysts to anti-fraud teams and researchers, rely on it to spot phishing campaigns early, protect their brand and move fast on takedowns.
Paste a URL, a domain name or an IP address and get an immediate answer from the last seven days of detections. It is free, protected by a CAPTCHA and needs no account. Try Web Search.
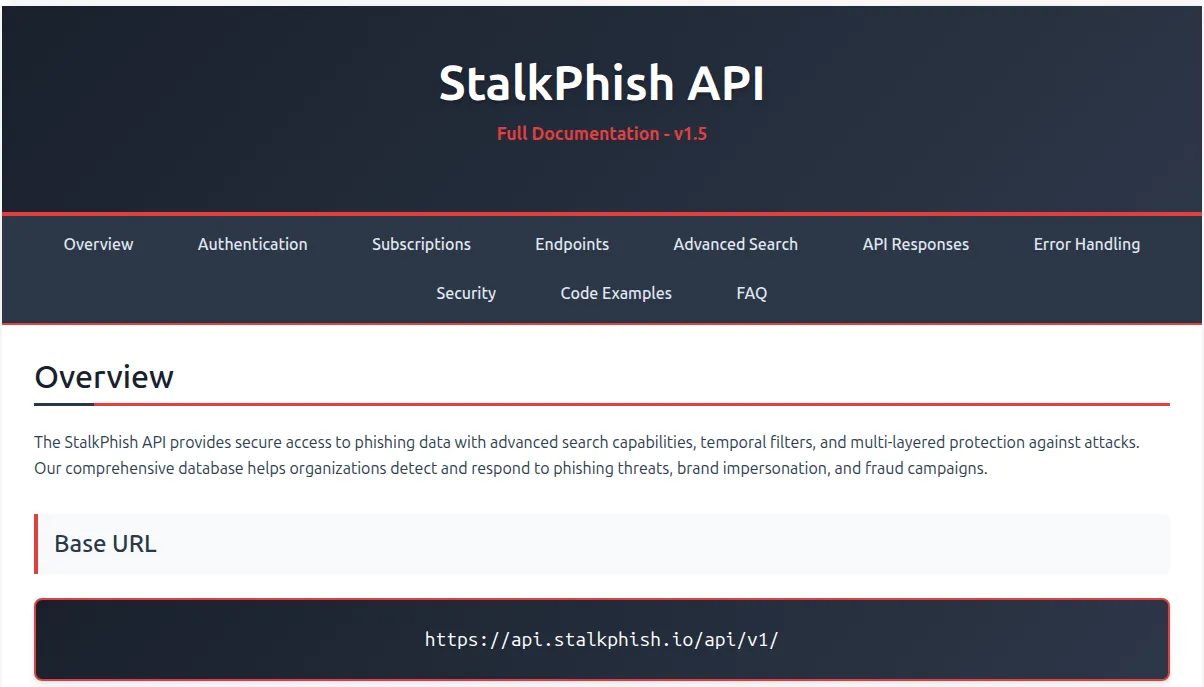
Everything the platform knows is available through a documented REST API, with an OpenAPI specification: search by string in URL, IP address, page title, brand, e-mail address, Telegram handle, favicon hash or kit archive hash, plus a feed of the latest detections, all with date filters.
curl -H "Authorization: Token YOUR_API_TOKEN" \
  "https://api.stalkphish.io/api/v1/search/brand/YourBrand?last_hours=24"
An abridged example of what a result looks like:
{
  "siteurl": "https://login-yourbrand-secure.example/portal/",
  "sitedomain": "login-yourbrand-secure.example",
  "pagetitle": "YourBrand - Sign in",
  "firstseentime": "2026-11-12T08:41:17Z",
  "firstseencode": "200",
  "ipaddress": "203.0.113.42",
  "asn": "64496",
  "asndesc": "EXAMPLE-HOSTING, NL",
  "targeted_brand": "YourBrand",
  "phishing_score": 87,
  "extracted_emails": ["drop@example.net"]
}
The API is made to be plugged into what you already run: SIEM and SOAR enrichment, an IntelOwl analyzer, CTI platforms such as OpenCTI or MISP fed by the latest-detections endpoint. 8 use cases for the StalkPhish API shows what teams build with it. Full details: API documentation.
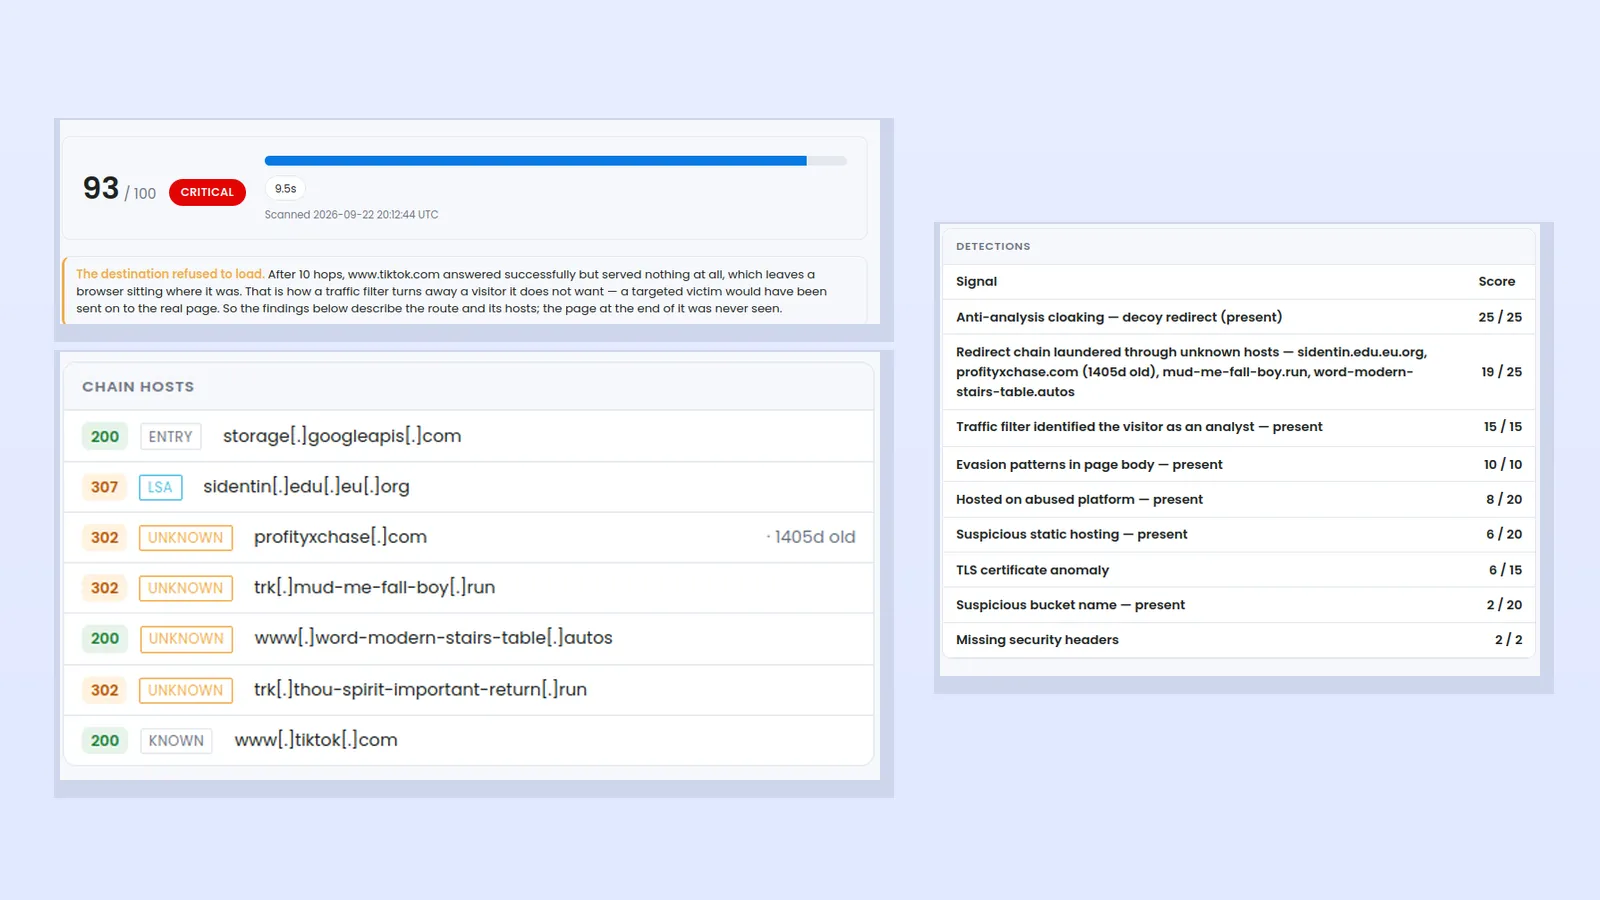
Our URL scanner follows a suspicious link to the end, through redirects and cloaking, and returns a threat score with the evidence behind it. It runs on the StalkPhish.io detection engine and is currently invite-only: read the presentation of the scanner and ask us for an access code.
From a free tier to evaluate the API to the Starter, Researcher, Standard and Professional plans, and an Enterprise plan on request. Every paid plan starts with a 7-day free trial; threat actor tracking and brand targeting are reserved for the Professional plan and above. Prices and limits are on the pricing page.
StalkPhish.io is the industrial version of the work we started in 2017 with open source tools: PhishingKitHunter, StalkPhish-OSS and the PhishingKit-Yara-Rules. The platform applies the same methods at scale, every day, and feeds the research we publish and the Dico du Scam. More about the company on the about page.
Check a suspicious link without opening it: the StalkPhish URL scanner follows redirects and cloaking, and gives a phishing score with evidence. Closed beta.
Brand protection, SOC enrichment, threat hunting, Telegram exfiltration tracking: eight practical ways to use the StalkPhish API against phishing and fraud.
Nouvelles techniques de smishing des escrocs francophones depuis 2025 : appels entrants, contournement des filtres et organisation des réseaux « au allo ».
Start with a free search, or talk to us about API access and custom intelligence for your brand.