Several domain names, one protected redirector, one phishing campaign
Sometimes phishing campaigns are not conduced with phishing kits only, actors behind those phishing campaigns can use different tricks to prevent their work being takedown, as using protected web redirectors.
A campaign we can see this days use this redirector trick on several domain names. This campaign target DHL customers, impersonating the delivery company.
A captcha protected redirector
More, the redirector is protected by a Google reCAPTCHA challenge:
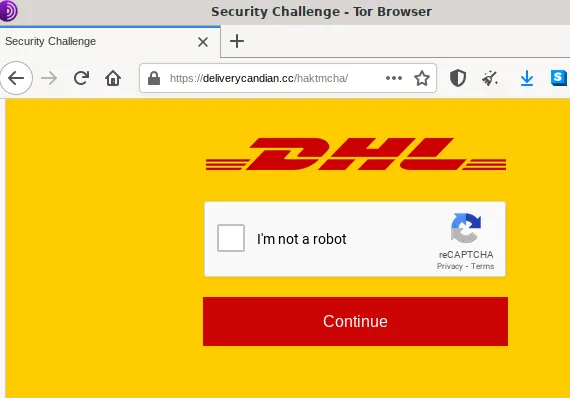
Google reCAPTCHA challenge
Like this a scraper, a robot, can’t continue behind this page to get the final landing phishing page.
Downloading sources with StalkPhish
With the help of StalkPhish (our open source phishing kit stalker), we can try to download the source code of pages if it is available somewhere, and bingo! we can find a zip file archive containing sources of this tool:
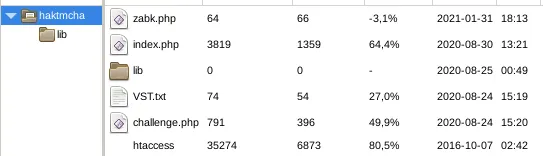
downloaded zip file content
The index.php file call the challenge.php one which present the captcha challenge, once the captcha completed and validated the zabk.php page
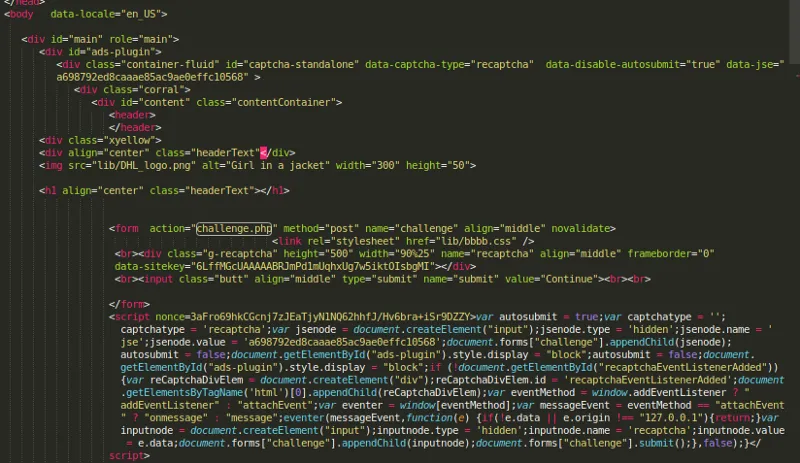
index.php file calling challenge.php
… is call which redirect the user to the landing page: hxxps://trakscloth.cc/manage/
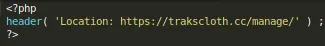
zabk.php file content
…which is - surprise - the phishing kit landing page (page we can’t show you because the domain doesn’t work anymore).
Pivoting on a string using StalkPhish
To have an idea of the magnitude of the campaign, you can use StalkPhish one more time to retrieve several informations about it, for that you can use the -s option of stalkphish with the name of the directory (haktmcha) the files are installed, as:
python3 StalkPhish.py -c conf/example.conf -s haktmcha
Then you can retrieve several domains and URLs where this redirector is, or was, installed:
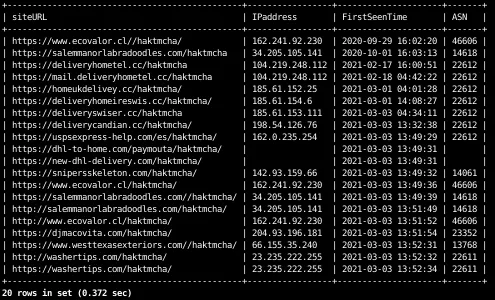
StalkPhish’s database extract
Using online app StalkPhish.io to find threat
You can also use the StalkPhish.io API to bust this threat. For that you just have to search for the exact same string (‘haktmcha’).
You need a API key for that, register for free there: https://www.stalkphish.io/accounts/register/
You can use this command to get data:
curl -H ‘authorization: Token your_API_Token_There’ https://stalkphish.io/api/v1/search/url/haktmcha
As is you can obtain several URLs where the redirector kit has been deployed and have an idea of who and where this campaign was targeting:
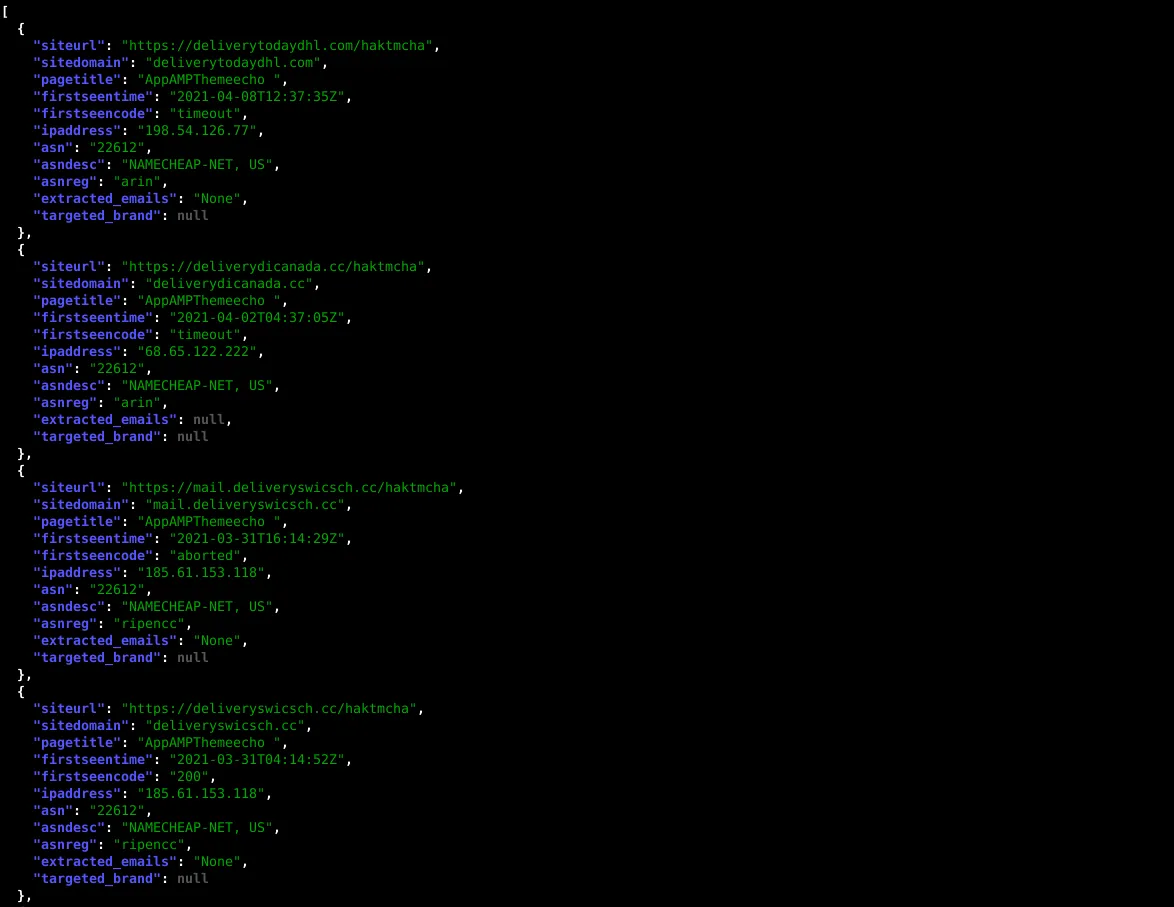
StalkPhish.io JSON data
Thank you!
Questions, or a similar campaign to report? Contact us.