· CERT
[StalkPhish.io] Phishing Kit family enrichment
StalkPhish.io now classifies the phishing kits it collects by family, using the open source PhishingKit-Yara-Rules, to speed up qualification and investigation.
Category
StalkPhish.io now classifies the phishing kits it collects by family, using the open source PhishingKit-Yara-Rules, to speed up qualification and investigation.
Analysis of the 'Don' phishing kit impersonating Caisse d'Epargne (BPCE group), downloaded by StalkPhish.io in December 2023: structure and configuration.
Short analysis of the Greatness phishing kit, a Phishing-as-a-Service tool targeting Microsoft 365 credentials and MFA, with original IOCs for hunting.
Teardown of the HadySpeed Coinbase phishing kit: a live admin panel lets the scammer interact with victims in real time to steal their 2FA codes.
Use case: detect phishing campaigns early by hunting phishing pages with StalkPhish, combining several data sources to find and take down sites faster.
A minimalist LinkedIn phishing kit written in Chinese: three PHP pages that email the stolen credentials, probably derived from a kit sold by Fudsender.
An M&T Bank phishing kit that sends stolen data to Telegram without a single line of Telegram code, through an etlgr.com email-to-Telegram relay.
Analysis of the 'Moha' phishing kit targeting suppliers of the Dubai Electricity and Water Authority: a self-contained 1.2 MB kit that logs its visitors.
How to load the open source PhishingKit-Yara-Rules into ClamAV to detect phishing kit ZIP archives with an antivirus you already run.
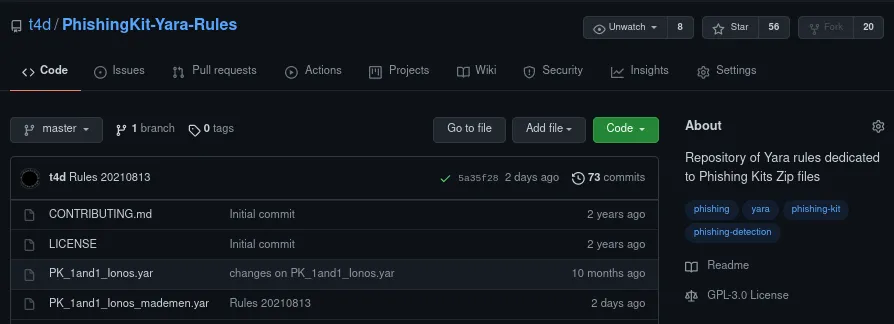
How the PhishingKit-Yara-Rules project detects and sorts the phishing kit ZIP archives left on servers, to speed up triage and extract actor information.
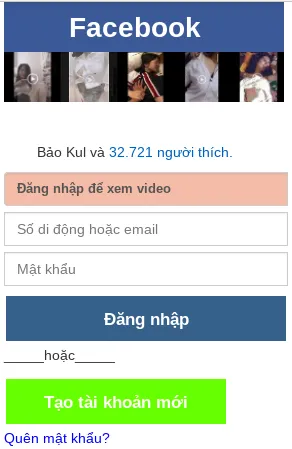
Analysis of a phishing kit targeting Vietnamese Facebook users, which sends the stolen credentials to an online Google Sheet with an AJAX POST request.